Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

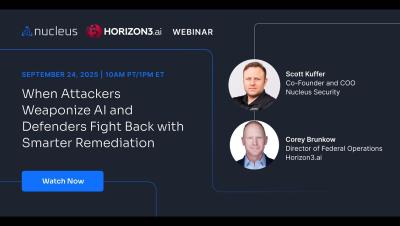
When Attackers Weaponize AI and Defenders Fight Back with Smarter Remediation

Artificial intelligence is transforming cybersecurity, and not always for the better. Attackers are now weaponizing AI to speed up reconnaissance, create exploit code, and bypass traditional defenses. Security teams can’t afford to rely on outdated vulnerability management practices. In this webinar, Scott Kuffer (COO, Nucleus Security) and Corey Brunkow (Director of Federal Operations, Horizon3.ai) break down how AI is changing the threat landscape and what defenders can do to stay ahead.

Zero Assumptions: A Data Science & Threat Intel Roundtable

How do data science and threat intelligence intersect to strengthen defenses in today’s evolving cyber landscape? Join us this Wednesday, September 24 at 10 AM ET for a special edition of Arctic Wolf SOCast: Zero Assumptions, where our experts will break down how advanced analytics and threat research work hand-in-hand to outpace attackers. Featuring.

Tools That Help You View Difficult Content Safely

When your job involves looking at distressing or graphic material, there are ways to reduce the impact. Therapist Eve Parmiter shares practical tools and techniques – like muting audio, using blur overlays, or limiting your screen view – that help professionals stay regulated while still doing the work.#CyberSecurity.

Have we reached true anonymous AI? #cybersecurity #ai

PromptLock ransomware represents a chilling evolution: AI that makes real-time decisions about your data. Unlike traditional ransomware that blindly encrypts everything, this malware uses a locally-hosted LLM to analyze file contents and decide whether to exfiltrate or encrypt based on what it finds. It's essentially agentic AI making autonomous threat decisions.

Security Potpourri: SOCs, automation, and penetration testing with Cliff Janzen

Cliff Janzen, CISO and VP of Security Services at Arctiq, joined us for Defender Fridays for a special "Security Potpourri" session! What's on the menu? > SOC operations and optimization> Security automation strategies> Penetration testing insights> The current state of security landscape> All through Cliff's expert lens and real-world experience.

Enrich, Parse, and Control Logs with Observability Pipelines for Datadog Cloud SIEM

See how Datadog Observability Pipelines helps security and operations teams take control of their log data. In this demo, we’ll walk through: With Datadog, you can normalize, enrich, and prepare high-quality log data for Cloud SIEM, supporting faster investigations, more accurate detections, and reduced operational overhead—all without third-party software.

Scattered Spider: the Evolution of Identity-Based Ransomware

Identity-based ransomware is no longer a fringe tactic; it’s becoming the playbook of today’s most dangerous adversaries. Scattered Spider, a financially motivated e-crime group, has shifted the model from smash-and-grab encryption to a far more devastating combination of double extortion, social engineering, and hypervisor encryption attacks.