Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

AppLocker Pros, Cons, and Alternatives

AppLocker is an application control feature found in enterprise editions of Windows. The tool enables you to manage which applications and files users can run. Windows AppLocker aims to limit software access and related data from specific users and business groups. The results of which is heightened security reduced administrative overhead and fewer helpdesk calls.
5 Top Local Administrator Password Solution (LAPS) Tips

The local Windows administrator account is a coveted target for hackers and malware. There are potentially a lot of bad things that can happen if a hacker can crack the local admin account of one of your servers. Dreadful things usually occur when someone downloads a malicious malware strain using the administrator account as well. The magnitude of these problems is amplified even more if you use the default administrator account for every similar machine uses the same password.

Splunk For OT Security: Perimeter And Vulnerability Evolution

Owners and operators of Operational Technology (OT) environments are being increasingly tasked with providing more information and security controls for their OT Environments, whether those demands are driven by the board, executive orders, or new regulations. One of the biggest fallacies that we encounter when our customers begin monitoring their OT environment is the idea that OT systems are air gapped and completely isolated from IT systems.

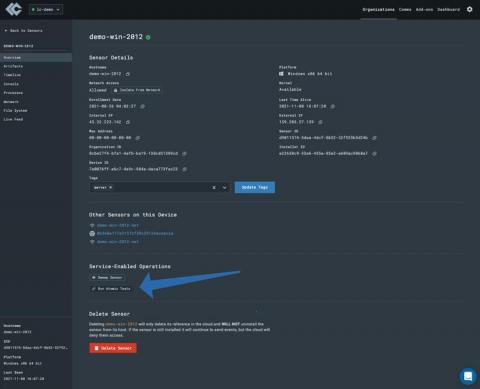
LimaCharlie & Atomic Red Team Enable a DevOps Approach to Cybersecurity

Engineering is both an art and a science. It requires creative thinking but is bounded by a rigidity which enables measurement and progress. We can only see so far because we stand on the shoulders of giants… and because those giants kept really good notes. Cybersecurity is growing up and it has to. Cyber is no longer the domain of shadowy figures in hoodie sweatshirts, it now has a presence in the C-suite.

SBOM Sharing Should be Easy. Now it is!

Today we’re pleased to announce the RKVST SBOM Hub – the first place to find and fetch SBOMs. RKVST SBOM Hub is a secure, immutable, any-to-any framework that integrates into both publisher and subscriber workflows to massively simplify the effective sharing of SBOMs to help all parties comply with the Executive Order. Try it out for yourself here.

Fuzz Testing in International Aerospace Guidelines

For obvious reasons, civilian aerospace is steeped in safety regulations. Long-standing international governing bodies mandate and oversee the specification, design, and implementation of civil avionics such that failure conditions that could lead to safety hazards are identifiable, assessed, and mitigated.

Deepfake technology and its implications for the future of cyber-attacks

Recently I received a call on my personal cellphone. The call started out as many do; with a slight pause after I answered. Initially I assumed this pause was caused by whatever auto-dialer software the spammer was using to initiate the call before their text-to-speech software starts talking about my car’s extended warranty. Once the pause was over, however, I was surprised by a very human voice.

What You Should Know About PCI Gap Assessment?

We know how complicated and resource-consuming it can be to comply with the standards set up by the PCI (Payment Card Industry) Security Standards Council. It’s not surprising that less than 1 in 5 businesses (around 18%) assess their PCI DSS controls more frequently than is required by the regulation. However, things become a lot easier and streamlined with PCI DSS gap assessment.

Java JSON deserialization problems with the Jackson ObjectMapper

In a previous blog post, we took a look at Java’s custom serialization platform and what the security implications are. And more recently, I wrote about how improvements in Java 17 can help you prevent insecure deserialization. However, nowadays, people aren’t as dependent on Java’s custom serialization, opting instead to use JSON. JSON is the most widespread format for data serialization, it is human readable and not specific to Java.

Phishing operators abuse bank APIs to improve phishing TTPs

True Login phishing kits are continuously being developed by threat actors to improve their TTPs in luring victims. By using true login kits, the phishing operators have a higher chance of making potential victims believe they are logging into the real website. True login kit developers are abusing publicly available APIs of the banking company to be able to query login information to be shown to potential victims, in turn luring the victim even further into the operations.