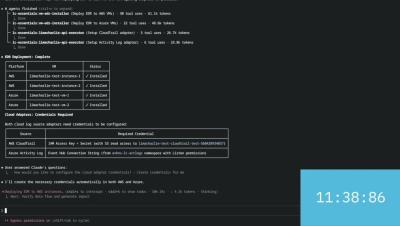
This video expands on the EC2 sensor deployment example by tackling a full customer onboarding across four cloud environments: AWS, Azure, GCP, and DigitalOcean.
When a new security incident surfaces, threat intelligence is only useful if you can act on it quickly. This video shows how Claude Code, combined with LimaCharlie, compresses that gap significantly.
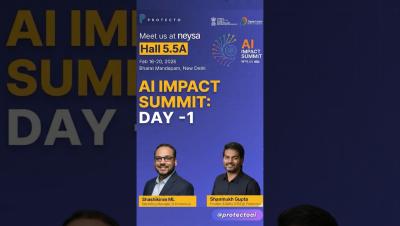
In this first official episode of our Event Diary series, we take you inside AI Impact Summit 2026 at Bharat Mandapam, New Delhi. We had the chance to interact with a massive range of AI leaders—from visionary startup founders and engineers to data and compliance teams at major enterprises. The biggest takeaway? Companies are looking for ways to fast-track their compliance and enable their data safely. At Protecto, that is exactly what we’re solving.
Last month, Microsoft quietly confirmed something that should keep every CISO up at night. As first reported by BleepingComputer and later detailed by TechCrunch, a bug in Microsoft Office allowed Copilot, the AI assistant embedded in millions of enterprise environments, to summarize confidential emails and hand them to users who had no business seeing them. Sensitivity labels? Ignored. Data loss prevention (DLP) policies? Bypassed entirely. This wasn't the work of a hacker or malware.
On February 9, 2026, security researcher Adnan Khan publicly disclosed a vulnerability chain (dubbed "Clinejection") in the Cline repository that turned the popular AI coding tool's own issue triage bot into a supply chain attack vector. Eight days later, an unknown actor exploited the same flaw to publish an unauthorized version of the Cline CLI to npm, installing the OpenClaw AI agent on every developer machine that updated during an eight-hour window.
Agentic AI is fundamentally changing how software operates, and in doing so, it breaks the identity and access models that many organizations still rely on. Unlike traditional applications, agentic systems are non-deterministic, long-running, and capable of autonomous decision-making across infrastructure, data, and production services. These systems do not fit within legacy identity assumptions built for humans, static workloads, perimeter controls, or long-lived credentials.
Your AI tools just became the perfect hiding spot for hackers. Cybercriminals have found a new attack vector: weaponizing the AI assistants your team uses every day. In this live demonstration, we show how adversaries can turn tools like Claude into persistent backdoors and how CrowdStrike Falcon stops them cold. TIMESTAMPS: WHAT YOU'LL LEARN:– How hackers exploit AI automation features to create backdoors– Why password resets and patches won't stop this attack– How behavioral detection catches threats hiding in legitimate tools– Real-time threat prevention in action.
Shadow AI models with weaker guardrails increase the power of already talented attackers and help less skilled users assemble dangerous campaigns. Frontier systems write malware when prompted as penetration tests, scale up attack speed and make it easier than ever to launch offensive operations against defenders. ⸻ For more information about us or if you have any questions you would like us to discuss email [email protected]. We give our clients a personalised, integrated approach to information security, driven by our belief in quality and discretion..
Global organisations face AI-enhanced cybercrime, record ransomware incidents, and an uptick in phishing attacks, highlighting the need for strong cyber defences.