Mailchimp
Not subscribed to OpsMatters Newsletter


The cybersecurity industry has spent a lot of time talking about improving the analyst experience without making significant improvements. Much of the effort has been too focused on trying to find a silver bullet solution. Combine that with a global pandemic and things are just getting worse.
The Splunk Threat Research Team (STRT) has been heads-down attempting to understand, simulate, and detect the Spring4Shell attack vector. This post shares detection opportunities STRT found in different stages of successful Spring4Shell exploitation. At the time of writing, there are two publicly known CVEs: CVE-2022-22963, and CVE-2022-22965. The Splunk Security Content below is designed to cover exploitation attempts across both CVEs.
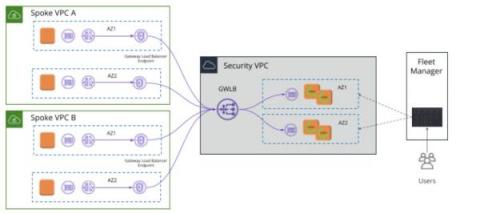
Corelight is pleased to announce our integration with AWS’s Traffic Mirroring to Gateway Load Balancer (GWLB) Endpoint as a Target. This integration simplifies the monitoring of network traffic and generating Corelight data in massively scaled-out public cloud environments. When it comes to monitoring network traffic today, we see two primary deployment patterns, each with their own pain points.
Instantly view your organization’s cybersecurity posture + continuously monitor and verify identity.