Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

You can't govern what you can't see: Detecting shadow AI on your network

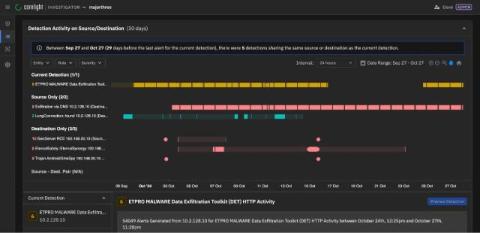
AI adoption inside the enterprise didn't ask for permission. It arrived through browser tabs, code editors, and meeting transcription bots, quietly stitching itself into daily workflows long before security teams could write policy around it. The result is a familiar story with a new villain, a sprawling, unmanaged attack surface that lives in your network traffic but nowhere in your asset inventory. We call it shadow AI, and it's the blind spot you didn't plan for or budget for.

What the Black Hat NOC taught me about MCP & agentic SOCs (Chapter 4 of 4)

The first time an MCP (Model Context Protocol) server felt real to me, it wasn't because of a clean demo. It was because of the noise. TL;DR: The harness matters more than the protocol, and the evidence matters more than both. MCP earns its keep when it shortens the path from a good security question to trustworthy evidence, and almost everything interesting about making that work happens in the harness wrapped around the model. In this series, I will cover how to build an MCP for an AI SOC.

What the Black Hat NOC taught me about MCP & agentic SOCs (Chapter 3 of 4)

The first time an MCP (Model Context Protocol) server felt real to me, it wasn't because of a clean demo. It was because of the noise. TL;DR: The harness matters more than the protocol, and the evidence matters more than both. MCP earns its keep when it shortens the path from a good security question to trustworthy evidence, and almost everything interesting about making that work happens in the harness wrapped around the model. In this series, I will cover how to build an MCP for an AI SOC.

Cleartext is all fun and games

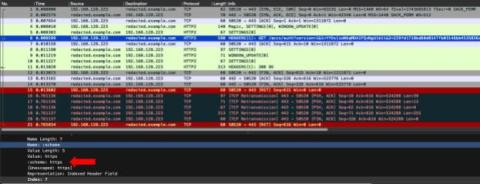
One of the many interesting things we stumble across in the Black Hat NOC (Network Operations Center) is the various applications exhibiting poor security hygiene. Usually it’s something in the clear that makes us chuckle before we move on to more serious matters. Sometimes it’s something more serious that requires letting an attendee know they’re leaking sensitive information.

Episode 19 - The Cap on Inference: Proving How Network Data Quality Drives AI Security ROI

In this episode, host Richard Bejtlich sits down with Corelight Co-founder and Chief Strategy Officer Greg Bell to unpack groundbreaking research that quantifies exactly how data quality impacts AI-driven security automation. Moving past qualitative industry hype, Greg shares hard evidence from an empirical experiment pitting leading AI agents against real-world Capture the Flag (CTF) challenges and incident response report writing. The findings reveal a dramatic truth: basic firewall and flow logs place a hard cap on inference, throttling an LLM's capacity for deep insight.

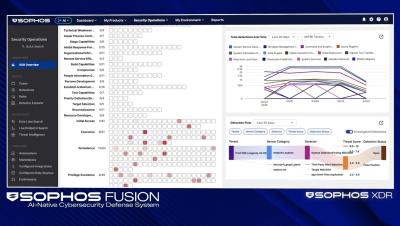
Sophos Launches Sophos Fusion, the Industry's First and Most Complete AI-Native Cybersecurity Defense System

Built for a threat landscape reshaped by AI, Sophos Fusion unites security operations, endpoint, network security, identity, email, and cloud into one defense system that prevents, detects, investigates, and responds at AI speed.

The State of Ransomware 2026: Payments are dropping but encryption is climbing

The State of Ransomware 2026: Payments are dropping but encryption is climbing Insights from 2,158 IT and cybersecurity leaders across 17 countries whose organizations were hit by ransomware in the past year. This year's data has a few eyebrow-raising departures from the patterns of past State of Ransomware reports. Exploited vulnerabilities lost their three-year grip on the top root-cause spot. Median ransom demands and payments both dropped, yet the average recovery bill still climbed.