Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

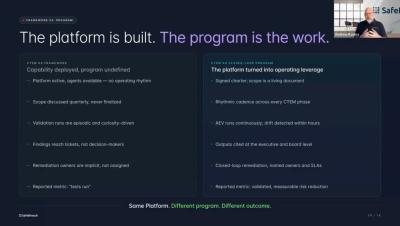
How Do You Operationalize CTEM and Prove It's Working?

Having the right security platform is only part of the equation. Two organizations can have similar security stacks and still achieve very different outcomes depending on how they operationalize their Continuous Threat Exposure Management (CTEM) program. In this video, learn what separates reactive, ad hoc security validation from a mature CTEM program—including: See how a structured CTEM program can turn continuous security validation into measurable progress across your organization.
What Campaigns Like Grandoreiro Teach Us About Threat Detection

The recent Grandoreiro campaign detected by the WatchGuard Threat Lab team is a clear example of how today’s threats combine different techniques to make detection more difficult and operate more discreetly. In this case, the attack begins with a phishing email designed to persuade the user to click a link. From there, the victim is taken through several redirects and eventually downloads a compressed file from well-known services such as Dropbox or MediaFire.

Domain Monitor Now Catches the Impersonation Attempts Keyword Matching Was Built to Miss

Domain Monitor's detection engine has been rebuilt to catch impersonation domains that keyword matching was never built to find. This release covers the new evidence-based matching engine, per-keyword Low, Medium and High thresholds, and what's coming next as the improvements roll out in stages. Domain Monitor's detection engine has been rebuilt from the ground up.

The Art of Detection Engineering: Why Great Detections Are Built with You

Out-of-the-box detection content gives security teams a strong starting point from day one. Its full value emerges when that content is tuned to reflect the users, systems, workflows, and risks unique to your environment. This article walks through why tuning matters, how mature security teams approach it, and how Securonix helps turn expert-built detection content into high-fidelity security outcomes.

Evaluating AI systems at Corelight

AI system evaluation is the process of continuously assessing AI system capabilities, limitations, and performance through quantitative and qualitative measures. Across the system lifecycle, evals provide continuous assurance: Validating system behavior before deployment and detecting drift, bias, and reliability issues in production.

Hunting the Undead: Accelerating NetNTLMv1 Lookups Without GPUs

Outdated protocols, forgotten configurations, and legacy dependencies continue to create opportunities for attackers in modern environments. This research explores how NetNTLMv1 can still be leveraged today and how improvements in attack tooling are reducing the cost and complexity of exploiting it.

Episode 21 - Building AI Harnesses to Unify Detection and Response

Corelight Senior Security Engineer Jordan Hair joins Richard Bejtlich to break down how defense teams can leverage agentic AI harnesses to transform traditional security operations. By wrapping deterministic code around large language models, Hare created automated agents for alert triage, threat hunting, and detection engineering that shrink routine investigations from 45 minutes down to seconds.