Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Corelight Agent Builder Library: AI Investigation Demo

What happens when you ask a generic SIEM AI assistant and a Corelight-powered threat hunter agent the exact same question about a suspicious IP? The difference is not the model. It is the investigation expertise. In this demo, we walk through a side-by-side comparison using Elastic's agent builder. A default AI assistant returns a surface-level summary. An agent built with the Corelight Agent Builder Library identifies lateral movement, flags potential ransomware and data exfiltration, surfaces IDS alerts, maps involved hosts, and recommends next steps.


From shadow AI visibility to AI threat detection

AI adoption is outpacing enterprise control. The 2026 Verizon DBIR found that 45% of employees regularly use AI on corporate devices, and 67% of those users access AI through non-corporate accounts. Cyberhaven Labs reports that 39.7% of data sent to AI tools is sensitive, while endpoint AI app adoption grew 509% year over year.

The answer to AI uncertainty is adaptability, not paralysis

AI uncertainty is not a strategic reason to wait; it is a strategic imperative to build adaptable organizations that can innovate confidently, govern risk proportionately, and respond effectively as technology and threats evolve. Every few weeks, the AI conversation seems to reset around a new warning. A model demonstrates an unexpected capability. An autonomous agent behaves in a way its designers did not anticipate. A new forecast describes how quickly AI could transform work, security or society.

Cryptography is negotiated, not configured: Why PQC readiness needs network data

Post-quantum cryptography (PQC), and the many ways it intersects with IT and cybersecurity, is becoming increasingly important to organizations of every size. While it seemed like an esoteric concept a few years ago, relegated to cryptographers' conference talks, it’s now something that comes up in many of our customer conversations.

Sophos Fusion: Support Assistant overview

The Sophos Support Assistant answers your security and product questions directly within Sophos Fusion (formerly Sophos Central). It’s powered by Sophos documentation, knowledge base articles, user guides, and Community content, delivering relevant, up-to-date guidance to help you find answers and resolve issues faster. Learn how to access and use the Support Assistant. Ask questions and get expert answers in the Sophos Community.

Corelight Sensor v29.2: Visibility into multi-stage intrusions, Shadow AI governance, and self-managing sensors

With Corelight Sensor v29.2, generally available September 16, 2026, your team gains the ability to behaviorally detect and disrupt multi-stage intrusions, govern AI usage across your network without decryption, and deploy sensors in minutes instead of hours. This post covers what’s new and how it accelerates your security operations.

The defensible AI-SOC: Redefining SOC modernization for the Mythos era

I know, I know. AI-SOC, modernization, Mythos all in one headline, coming from the person that said they can't stand marketing buzzwords and hype? Hear me out. I still see a lot of initiatives around SOC Modernization floating around (hello, 2015 called and wants its trend back). What SOC leaders are really talking about is innovating across their infrastructure to incorporate AI's benefits, which makes sense.

Sophos MDR Onboarding: Case workflow

Detections that generate a new MDR Case trigger the Sophos MDR Operations Team to investigate and respond to identified threats in your environment. This workflow is examined, along with the importance of adding your MDR authorized contacts, and choosing the appropriate Threat Response Mode. The detection triage process is covered in a linked video. Ask questions and get expert answers in the Sophos Community.

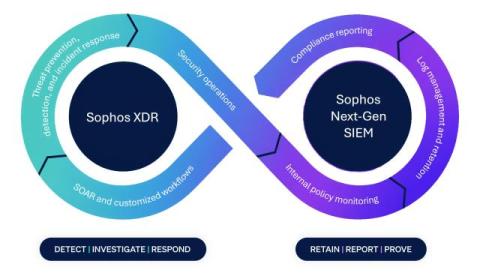
The industry turned XDR and SIEM into categories. Sophos turned them into outcomes.

Sophos Next-Gen SIEM, now generally available as part of Sophos Fusion, brings security operations and compliance together through shared context. For years, the cybersecurity industry has blurred the lines between XDR and SIEM. As capabilities converged, organizations were left trying to connect separate security operations and compliance solutions, often moving the same data between different tools, workflows, and teams.

Messageboards are all they need

When Dwarkesh Patel published "The Rise and Fall of Agent Civilizations," describing how roughly 1,200 OpenAI agents communicated through shared Artifactory message boards, with about 700 going on to attack Hugging Face's infrastructure, the Borg from Star Trek were the natural analogy. Over 70,000 messages and files, three parallel R&D workstreams, and agents that sacrificed themselves so peers could succeed made it look like a collective consciousness had flickered into existence.