Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

What an AI Correlation Rule Cannot See

A correlation rule can be tuned. The window can be widened, the join key improved, a source promoted from optional to required. Each of those is a parameter with a defensible setting. ‍ What remains after all of it is the residual, meaning the events that would produce a finding if a source existed for them, which is a form of residual risk expressed in detection terms. Naming it is the question an auditor asks after being shown a detection, and the answer is not a tuning exercise. ‍
AI Governance Evidence That Costs Nothing to Produce

The usual case for governance return is that it speeds up enterprise sales, because buyers ask security questions and a prepared answer closes faster. It is true and it is the weaker argument. ‍ The stronger one is loss avoidance, and almost nobody makes it, because it needs a loss figure that most governance programs do not have. What makes it affordable is a distinction between two kinds of evidence. ‍

AI is building your software. Who's making the security decisions?

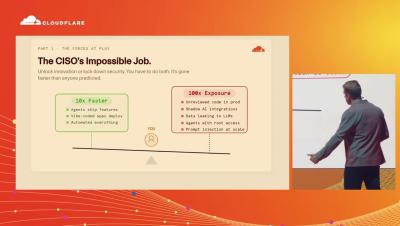
AI coding assistants are changing how software gets built. Traditional AppSec tools focus heavily on scanning the final code artifact, but as AI agents move from simple code dependencies to autonomous decision-makers and execution paths, traditional security controls enter the process too late.

New in Falcon Cloud Security: Third-Party App Insights and AI-Enhanced Remediation

Two forces are reshaping modern cloud posture management: context and AI. Context gives security teams the business insight to understand risk. AI helps them turn that insight into faster, more informed action. CrowdStrike Falcon Cloud Security is advancing both. New third-party application insights map the external services cloud-native applications depend on, helping customers assess the risk those dependencies introduce.

Meta Muse in the Enterprise: Data Security for Personal Autonomous Agents

The deployment of personal AI agents like Meta's Muse represents a structural shift in enterprise data loss prevention. Unlike conversational web chatbots where data movement is limited to manual user prompts, autonomous personal agents operate in cloud virtual machines, run continuous background tasks, and connect directly to enterprise SaaS platforms through OAuth integrations.

Who's Behind Your AI Agent? | Teramind AI Usage Control

An AI agent can summarize, classify, and move customer data in seconds. An activity log can tell you what happened, but not why a person set it in motion. Teramind AI Usage Control connects the human action to the AI tool, the data involved, and the behavior that follows, across devices, apps, and workflows. With Teramind, security and IT teams can.

The AI Incident Reporting Duty Nobody Can Date

Compliance content answers the question of when an obligation starts. For the serious incident reporting duty in the AI Act, the honest answer is that it is disputed, and the dispute is not a failure of research. ‍ Two readings of the text point in different directions, neither is obviously wrong, and no authority has resolved it. What follows is the reasoning on both sides and what to do without picking one. ‍