A strong vulnerability management program underpins a successful security strategy overall. After all, you can’t defend weak points you don’t know are there. It is predicted that 2023 will see an average of 1,900 critical Common Vulnerabilities and Exposures (CVEs) a month, up 13% from last year. This is due to increased interconnectedness, the addition of more tools, IoT devices and SaaS services, and the increased risk of human error.
A few years ago, I wrote about the importance of security immutability. More specifically, I discussed how important it is that your environment be unchangeable in order to ensure that it remains secure. As I looked back on the article, I found it rather amusing that the article was published 4 years ago, but that feels like a lifetime ago. In the last few years, we really have seen just how volatile the world can be.
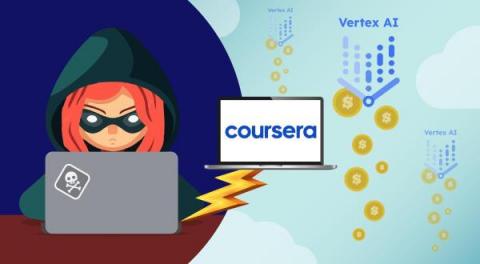
The Sysdig Threat Research Team (Sysdig TRT) recently discovered a new Freejacking campaign abusing Google’s Vertex AI platform for cryptomining. Vertex AI is a SaaS, which makes it vulnerable to a number of attacks, such as Freejacking and account takeovers. Freejacking is the act of abusing free services, such as free trials, for financial gain. This freejacking campaign leverages free Coursera courses that provide the attacker with no-cost access to GCP and Vertex AI.
A typical security operations centre (SOC) has three core costs: People, data and tools. The total cost of these will vary dramatically based on factors like how many endpoints and users are in your environment and the number of SOC team members you need. Various SOC cost calculators available online put the cost of building a SOC for a 1000-user environment at upwards of £2 million per annum.
In July, we released Private Integrations which allow you to connect any app to Vanta, plus 30 new integrations, additional customization for pre-built Vanta content, and more: