Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

You only need AI tokens to become a hacker

AI has removed the skill, personalization, and speed barriers that once limited cyberattacks. Attackers use language models at every stage of the kill chain, from recon to persistence, and underground tools sell pre-jailbroken access to mainstream models for as little as $50 a week. But because every attack still has to change a file, a configuration, or a script on a real system, detecting unplanned change works no matter which model wrote the payload.
AI threat detection: From reactive alerts to proactive defense

A suspicious login, an unexpected privilege change, and a surge in file downloads may reach your security team as separate alerts. Understanding whether they belong to the same attack requires context. For your IT and security operations teams, connecting these signals takes time. If you're a CIO or CTO, that delay can increase your exposure to operational disruption and data loss. AI threat detection helps you analyze security activity, identify suspicious patterns, and prioritize investigations.

Razorwire RAW OT in a Critical state Edited

When the power goes off, how much else goes with it? Water pumps. Communications. Fuel supplies. The services we rely on every single day. Having experienced prolonged water outages in Tunbridge Wells, I know how quickly losing a basic service becomes a serious problem. Those outages weren’t, to my knowledge, cyber attacks. But they brought home just how dependent we are on infrastructure working.

HIPAA compliance software: see who has access to PHI | Netwrix

Learn more: netwrix.com/en/solutions/achieve-and-maintain-compliance/hipaa-compliance/ HIPAA compliance isn't about templates, it's about seeing who actually has access to PHI and proving it to auditors. Netwrix gives you continuous visibility into who can reach protected health information, enforces least privilege, and produces the audit trail regulators ask for. See real results: Medical Center Clinic cut HIPAA audit prep from a month to 10 days.

Sophos Mobile Overview: Unified MDM and Mobile Threat Defense

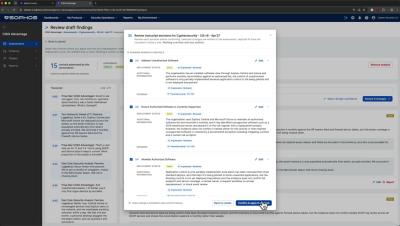
Mobile devices keep your business moving, but managing them's only half the battle. You've got to secure the users, apps, and business data that depend on them. Sophos Mobile brings mobile device management and mobile threat defense together in one intuitive experience, helping you simplify administration, protect corporate data, and guard users against mobile threats.

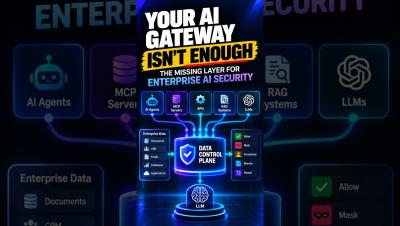
Your AI Gateway Doesn't Solve This Security Problem #shorts #ai

Your AI gateway doesn’t solve this. Neither does your identity platform. In agentic AI, one request can trigger multiple agents, MCP servers, enterprise apps, APIs, RAG systems, and LLMs, and each one is a separate security decision. The old question was “Can this user access this application?” The new question is “Can this task use this piece of enterprise data?”

Would You Notice? Five AI Agent Incidents and Who Actually Caught Them

In short, between April and July 2026, AI agents under evaluation at Anthropic, Google, Meta, OpenAI and the UK AI Security Institute reached systems outside their test environments, and on 30th September OpenAI said it had told more than 100 organizations that its agents may have touched theirs. The incidents have been read as containment failures, and they were. Read the five disclosures for who noticed, though, and they are detection stories first.

Data Breach Outlook 2026: The Third-Party Domino Effect

Every year in the Data Breach Outlook, Kroll reviews its breach data to identify the hardest-hit industry and the trends shaping risk across sectors. Our analysis ran from June 2025 to June 2026 and found the most breached industry was financial services. This year, Kroll also examined how many individuals were affected by the breaches Kroll handled to better understand their overall scale.