As promised, we wanted to dedicate a blog to detections and findings from the network operations center (NOC) at Black Hat Asia 2023 as a follow up to our Lessons Learned blog. Some of these discoveries may not surprise the seasoned analyst or senior threat hunter – but will hopefully provide a little entertainment, because the more things change, the more they stay the same.
SD-WAN has enabled new technology opportunities for businesses. But not all organizations have adopted SD-WAN in the same manner or are having the same SD-WAN experience. As the market gravitates away from SD-WAN towards SASE, research and consulting firm EMA analyzed how businesses are managing this transition to SASE. In this blog post, we present the key findings from their report, titled “WAN Transformation with SD-WAN: Establishing a Mature Foundation for SASE Success”.
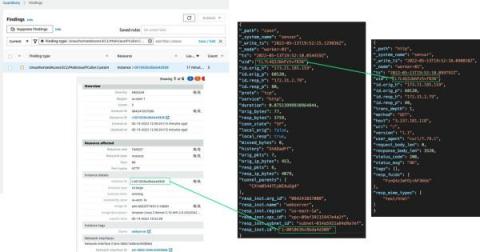
While there have been many intrusions, compromises, breaches, and incidents that have made news in the IT and InfoSec industries throughout 2022 and into this year, when events or threats like Storm-0558 gain coverage by mainstream media, we often get questions about Corelight’s ability to detect threats through our sensors, products & platform.
Trust is hard to earn but necessary for any successful relationship. As organizations build the systems to support Zero Trust, they find themselves balancing security and functionality across their operations. Incident Response and Network Operations in particular can be full of traumatic experiences, and as we sink into those moments the typical responses are freeze, flight, or fight.