Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Check Point Exposure Management Safe Remediation Demo: Harden Firewalls, Endpoints Operating Systems

Closing an exposure should not cause an outage. See how Safe Remediation in Check Point Exposure Management turns findings into validated fixes on the security controls you already own, without business disruption.
Zenity Launches Universal Runtime Control for Claude Enterprise

Anthropic's Inference Hooks update lets security teams validate Claude's tool calls before they run. Zenity supports it across Claude's surfaces, so teams can approve write-capable connectors, Model Context Protocol (MCP) servers, and wider Claude Code rollouts with policy on each action.

Architecting Trust: The Data Pipelines and Infrastructure Behind The Guardian Agents

As AI agents operate with increasing autonomy in enterprise production, the sheer volume of security telemetry they generate creates an unprecedented scaling challenge. Human oversight remains required in many enterprises, while legacy triage tools simply can't keep up. To help security teams cut through the noise, Zenity’s AI group built the Blue Agent.

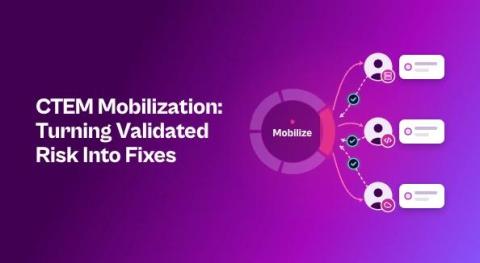
CTEM Mobilization: Turning Validated Risk Into Fixes

Mobilization is the fifth and final stage of continuous threat exposure management (CTEM). It turns validated, prioritized exposures into action by assigning clear owners, delivering context-rich work into the tools teams already use, choosing the fastest safe response, tracking SLAs, and verifying that fixes worked. It’s often the hardest stage because security teams find exposures but IT, engineering, and cloud teams fix them.

Between a Rock and a Hard Place: When Dependency Cooldowns and CVE Policies Deadlock the Build

On a recent call, a security lead walked us through two rules his team enforces on every build. Both are sensible. Together, they left his developers with a red pipeline and no version of a library they were allowed to use. The first rule is a cooldown. A new open source release cannot enter the build until it has been public for a set number of days. The second rule blocks any library version with a known high or critical vulnerability.

How Autonomous Pentesting Makes Hunting Business Logic Vulnerabilities Cheaper

For the ten years I have watched this industry, hunting business logic vulnerabilities has been notoriously expensive and exceedingly difficult. Every attempt to bring the cost down has hit the same wall. Now, for the first time, we as an industry have the capability to meaningfully lower the ceiling on what this work costs. I would argue Astra’s autonomous pentesting platform is pioneering that shift.

LearnUpon Pricing: What Influences It?

LearnUpon pricing requires a direct conversation because the published listing does not show a fixed starting rate or package breakdown. The available information identifies a subscription-based, paid Learning Management System (LMS) model with no free trial and directs prospective buyers to contact the provider. Understanding these details early helps avoid budget surprises later.