Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Web Application Security Checklist

In this digital age, web and mobile applications have become more complex. While developers are pressured to quickly develop/ update apps and release new features, IT security teams and organizations have a tough time keeping security risks under control. We have put together a web application security checklist to help organizations strengthen their application security in the current threat environment.
Securing the Digital Supply Chain Ep. 10 - Peeyush Ranjan

An amazing conversation with Peeyush Ranjan, Engineering VP at a Fortune 50 organization. Peeyush coined an amazing term - "Diffused Responsibility" - this is the reason why we all, in different silos, development, security, GRC, legal have to try harder and pull towards the same goal. In fact the example used - of a sports team, getting the pigskin over the line is a very apt one.

Four steps for securing a multi-cloud environment

The total number of mission-critical applications running in public clouds almost doubled between 2020 and 2022, and we expect this growth to continue. With this statistic in mind, no one argues against the need to prioritize securing multi-cloud estates. Public cloud providers such as Amazon Web Services and the Google Cloud Platform have significant resources and expertise dedicated to cloud security. But what are cloud providers actually responsible for securing vs. what an IT team needs to manage?

Meeting PCI DSS Third-Party Risk Requirements

Organizations must enact effective third-party risk management (TPRM) programs to ensure their vendors fulfill cybersecurity requirements. Otherwise, they risk carrying the financial and reputational harm caused by customer data breaches. The PCI DSS standard covers aspects of third-party risk management as it's applicable to all organizations that process credit card data, especially the heavily regulated finance industry.

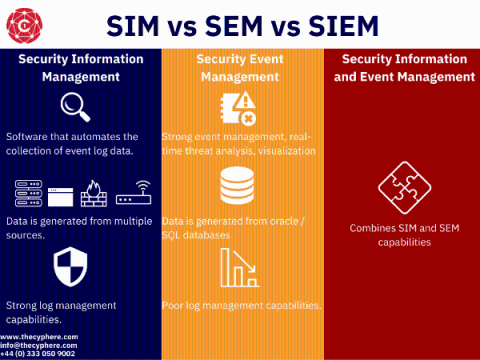
What is SIEM? A guide to cyber Security Information and Event Management

Security information and event management refer to Security Information Management (SIM) and Security Event Management (SEM) through a single pane of glass. SIEM solutions are used by security analysts to monitor any potential threats within the infrastructure of their organisation.

Network attacks, the protagonists of the latest Internet Security Report

Today’s threat landscape is evolving rapidly. Attackers are constantly adjusting their tactics and finding new ways to infiltrate organizations with increasingly sophisticated attacks to steal valuable data. As such, businesses and IT professionals must remain up to date on the industry’s latest threat intelligence in order to better understand the current state of this cybersecurity landscape and know their enemies to shore up defenses.

Choosing the Right Metadata Store: Part 3

Part 1 of this series covered the challenges Rubrik initially faced with its distributed database. Our applications had become quite complex to work around some of these challenges. Part 2 of this series covered how we chose a new distributed database (CockroachDB), and how we performed the migration. Next, we will dive into some of the challenges we faced after migrating to CockroachDB and how we developed on top of CockroachDB to mitigate them.