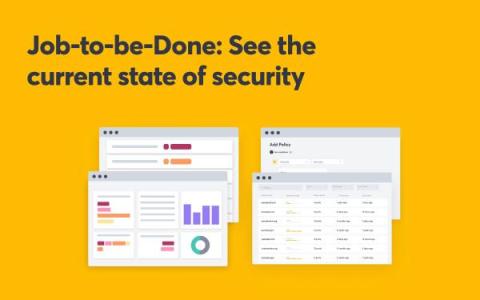
New assets, vulnerabilities, and even human errors like server misconfigurations make a continuously updated overview non-negotiable. AppSec and ProdSec teams must take action on newly discovered vulnerabilities and policy breaches quickly and efficiently. Prioritizing which vulnerabilities and risks to remediate first and having this information all in one place will help security teams get the latest insights about their attack surface immediately.
Kroll has observed an uptick in cases of DARKGATE malware being delivered through Microsoft Teams messages. These campaigns have mainly targeted organizations in the transportation and hospitality sectors. This activity has also been reported throughout open-source reporting, sharing a number of key indicators with Kroll observations, such as common filenames, adversary infrastructure and similar domain name conventions to host the initial download.
In my role as an Inside Solutions Architect at 11:11 Systems, my objective is to match 11:11 Systems range of solutions to meet customer’s data protection needs, from simple off-site BaaS to fully managed DRaaS solutions. That objective is easier to achieve when customers come to the table with an effective and reliable recovery plan. So how do you make an effective and reliable recovery plan? Here are a couple of key consideration points when constructing your recovery plan.
Earlier this year, we introduced the LimaCharlie SecOps Cloud Platform (SCP). The SCP is a unified platform for modern cybersecurity operations. Similar to what the public cloud did for IT, the SCP offers security teams core cybersecurity capabilities and infrastructure: on-demand, pay-per-use, and API-first. In short, the SCP is a new paradigm for cybersecurity. It’s a game-changer for enterprise security teams and cybersecurity solutions builders.
Back to school is a great time to remember basic cybersecurity best practices to protect you and your family. These won’t surprise anyone who’s been parenting for the last few years, but what might surprise you is how fast things are changing, which can increase your risk of giving access to cyber criminals. That is mostly around all the applications, and even micro-applications, that most frequently provide the lowest levels of security.