Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Social Engineering Campaign Uses Phony NDAs to Avoid Detection

Researchers at Gen Digital are tracking a sophisticated social engineering campaign that’s using phony NDA documents to trick employees into moving the conversation to WhatsApp and personal email accounts. The attackers targeted an employee at Gen itself, but the employee recognized that it was a scam and played along to see what the attackers would do. The threat actors first impersonated a real Gen executive based in Dublin, who introduced a second impersonated person who claimed to work at PwC.

Warning: "Slop Squatting" Directs AI Users to Phishing Pages

Threat actors are increasingly leveraging AI hallucinations to plant phishing links and other malicious content in AI output, IEEE Spectrum reports. Large language models (LLMs) sometimes fabricate information, including web domains, when answering users’ questions. Attackers are registering these hallucinated web domains to host phishing pages.

Device inventory is not privileged account discovery

A device inventory tells you where the machines are, while a privilege inventory tells you where an attacker can go. An endpoint record can show that a machine exists, who owns it, and whether a management agent has checked in. It does not show who can administer that machine. That distinction matters because an attacker doesn't need a complete asset inventory. A valid privileged path to one useful endpoint may be enough.

What Is ML-KEM? Guide to NIST's Post-Quantum Key Encapsulation Mechanism

Quantum computers are likely to render the current public-key cryptography used for protecting modern internet traffic, digital signatures, and encryption useless. In response, NIST has developed ML-KEM as the main post-quantum key encapsulation method. The guide below will introduce the concept of ML-KEM, how it functions, in which projects it is used, and how organisations can implement it.

Reporting a Vulnerability in Somebody Else's Code

A vulnerability in an open-source library inside your product is your vulnerability to report. The duty follows the product to market rather than the code to its author, so integrating somebody else's component transfers the obligation to whoever ships it. ‍ The reporting is the visible half. The harder consequence is that the same regulation requires remediation across the product in its entirety, and the party who wrote the component may have no obligation to help you. ‍

Evidence for One AI Framework Does Not Count for the Next

An organization assembles an evidence package for one AI framework, passes, and discovers that almost none of it transfers to the next instrument applying to the same system. The frameworks agree on the principles and disagree on what proves them. Three frameworks defining risk differently is the same problem one layer earlier. ‍ The common response is to look for a crosswalk and treat the mapping as a reuse plan.

Emerging Threat: (CVE-2026-78006) The Events Calendar Remote Code Execution via PHP Object Injection

CVE-2026-78006 is a deserialization of untrusted data vulnerability (CWE-502) in The Events Calendar, a WordPress plugin published by StellarWP, that allows an attacker to achieve remote code execution on the underlying host. The flaw sits in the is_safe_widget_instance function, whose guard against unsafe object data can be bypassed.

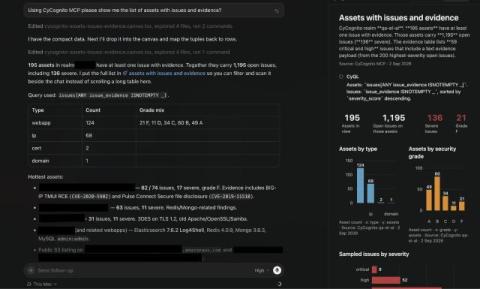
Introducing the CyCognito MCP Server: Full Exposure Context, On Demand

Today we are happy to announce the beta release of the CyCognito MCP server, which makes your external attack surface data consumable by any AI client that speaks the Model Context Protocol, including Claude, Cursor, and ChatGPT. The server runs on CyQL, the proprietary query language behind advanced search in our platform. CyQL is designed to ask precise questions about an attack surface, using operators suited to each type of asset, issue, and relationship.

AI Agent Security Readiness: The Federal Standard You Should Get Ahead Of

Here's the uncomfortable part first: in August 2026, researchers found AI agents connected to Hugging Face running loose inside enterprise networks. No owner, no audit trail, nobody who could tell you they existed until something broke. If that sentence made your stomach drop a little, good, because it should. It's the same blind spot most security teams are sitting on right now. They just haven't had their version of the incident yet.

Good Security Rating? Your Dark Web Exposure Says Otherwise

Ask a security leader how secure their company is, and most will point to a number. A rating, maybe a grade, or a score out of some maximum that a vendor calculated for them. That number only measures half the problem. It tells you about your infrastructure: your email configuration, your encryption, what's visible on the internet. It tells you much less about whether your employees' credentials are already exposed to an attacker.