Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Log4Shell in a nutshell (for non-developers & non-Java developers)

If you’re in tech at all, you’ve likely heard of the Log4Shell exploit taking over the Intertubes. If you’re not a Java developer (or developer of any sort), you may be left scratching your head as to just what’s going on. This post is split into two parts: an explanation of Log4Shell for non-developers and an overview of the Log4Shell vulnerability for non-Java developers.
Exploiting, Mitigating, and Detecting CVE-2021-44228: Log4j Remote Code Execution (RCE)

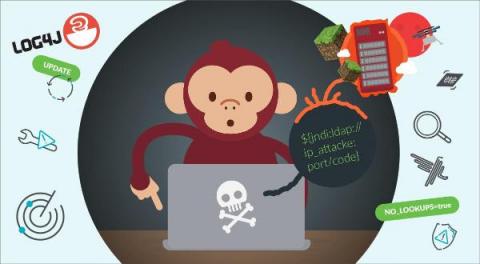
A new critical vulnerability has been found in log4j, a widely-used open-source utility used to generate logs inside java applications. The vulnerability CVE-2021-44228, also known as Log4Shell, permits a Remote Code Execution (RCE) allowing the attackers to execute arbitrary code on the host. The log4j utility is popular and used by a huge number of applications and companies, including the famous game Minecraft.

7 Security Operations Center (SOC) Best Practices for Analysts

Security ratings are becoming a crucial component of every security operations center (SOC). Security analysts must learn how to read, analyze and report security ratings to the CISO effectively in order to help build an enterprise-wide culture of security. Here we outline how analysts can develop a successful security operations center that leverages ratings to evaluate and mitigate cyber risk.

Survey Underscores Challenges Companies Face in Managing Vulnerabilities

Vulnerability management remains a struggle for many companies and is still only an aspiration for many others. But with digital and cloud transformation rewriting the way many firms do business, the attack surface keeps expanding and becomes more difficult for organizations to protect their environments from growing threats.

Press information: Crowdsource hacker first to find Zero-Day CVE-2021-43798 in Grafana

The vulnerability, dubbed CVE-2021-43798 impacted the Grafana dashboard, which is used by companies around the world to monitor and aggregate logs and other parameters from across their local or remote networks. The privately reported bug became a leaked zero-day but was first spotted by Detectify Crowdsource hacker Jordy Versmissen on December 2, after which Grafana was notified by Detectify about the bug.

How CrowdStrike Protects Customers from Threats Delivered via Log4Shell

Recent CrowdStrike Intelligence team findings regarding the Log4Shell (CVE-2021-44228, CVE-2021-45046) vulnerabilities indicate wide-ranging impact. CrowdStrike helps protect customers from threats delivered via this vulnerability using both machine learning and indicators of attack (IOAs).

CVE-2021-45046: New Log4j Vulnerability Discovered

Shortly after the Apache Software Foundation (ASF) released the bug fix for the vulnerability known as Log4Shell or LogJam (CVE-2021-44228), a new vulnerability was discovered in Log4j Java-based logging library, tracked as CVE-2021-45046. While Log4Shell had the maximum CVSS score of 10, this new vulnerability is rated as 3.7, affecting all versions of Log4j between 2.0-beta9 and 2.12.1, as well as between 2.13.0 and 2.15.0.

58% of Orgs Are Using a Vulnerable Version of Log4j

On December 9, 2021, a zero-day vulnerability in Log4j 2.x was discovered. This vulnerability is of great concern because if it’s successfully exploited, attackers are able to perform a RCE (Remote Code Execution) attack and compromise the affected server. Since we are a cloud-based Software Composition Analysis (SCA) provider, we have useful customer data that gives insight into the scope of the Log4j vulnerability.