Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

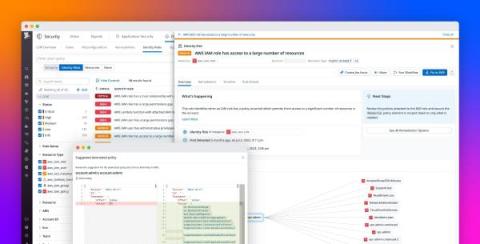
Find and remediate identity risks with Datadog CIEM

Identity and access management (IAM) systems are necessary for authenticating and authorizing access to your environment. However, their mismanagement is one of the leading causes of breaches and insider threats today. Engineering teams must rapidly provision identities and permissions to keep pace with infrastructure growth—consequently, the ratio of non-human or machine identities to every human identity is also increasing at a substantial rate.
Making the cloud the safest place to compute: Sumo Logic Cloud Infrastructure Security for AWS

The landscape of cloud computing has evolved significantly over the years, transforming how businesses operate and innovate. This transformation has brought new challenges, especially in security. The growing adoption of cloud services, microservices architecture, and the shared responsibility model of cloud vendors has ushered in a need for robust security solutions that consolidate risk and threat data across cloud environments.

Black Friday: Loved by Shoppers and Fraudsters Alike

For some, Black Friday conjures images of parasite-infected shoppers running amok in a mall. (Rotten Tomatoes gives the movie a 65% rating). For bargain hunters, it is a whirlwind of unbeatable deals and frenzied shopping sprees. Thanksgiving Day, Black Friday and Cyber Monday are the year’s biggest days for American merchants. The hype has crossed borders.

Exploring WebExtension security vulnerabilities in React Developer Tools and Vue.js devtools

Snyk's security researchers have conducted some research to better understand the risks of WebExtensions, both well-known (i.e. XSS, code injection) and those more specific to WebExtensions themselves. From our research we identified and disclosed some vulnerabilities within some popular browser extensions: React Developer Tools and Vue.js devtools. In this post, we will explore the WebExtension technology and look into the vulnerabilities identified.

Gift cards or data theft? Ensuring safe online shopping this festive season

Gift cards have become a go-to Christmas present for many people, but their dramatic rise in popularity has also unfortunately made them a prime target for hackers. The reason why gift cards are such a popular present is because of how practical they are to use. When you’re not sure what to buy someone, gift cards present an easy and accessible way to show someone how much you appreciate them.

NIST NCCoE Publishes Cybersecurity Framework Profile for Hybrid Satellite Networks

In late September 2023, the US-based National Institute of Standards and Technology (NIST) published its Cybersecurity Framework Profile for Hybrid Satellite Networks, otherwise known as NIST IR 8441. This blog will explore the reasons behind NIST developing the framework, outline its intentions, and summarize its key points.

Guarding the Grid: Navigating the Current and Future Landscape of Utility Cybersecurity

Tripwire recently held its annual Energy and NERC Compliance Working Group. This year's attendees included more than 200 Tripwire customer utility personnel representing over 80 different registered entities from all across the US and Canada. The company sizes ranged from public utility districts and city municipalities to medium and larger-sized investor-owned utilities, including many of the Fortune 500 and 1000 power entities.

How to Create an Effective Vendor Onboarding Policy

Forming partnerships with new vendors can be a complicated and risk-intensive process for any organization. The best way to manage the risks associated with new partnerships and establish successful vendor management practices is to create an effective vendor onboarding policy. Organizations create vendor onboarding policies to standardize the onboarding process, streamline vendor evaluation, and manage vendor risk and vendor compliance.

LDAP Cybersecurity Risks and Prevention Techniques

LDAP, which stands for Lightweight Directory Access Protocol, provides an open-source, vendor-neutral application protocol for distributed directory services and user authentication. This article provides a brief overview of LDAP uses, followed by a description of LDAP exposure risks and cybersecurity protection strategies.

CVE-2023-43177: Critical Unauthenticated RCE Vulnerability in CrushFTP

On August 10, 2023, CrushFTP released an advisory regarding a vulnerability affecting versions of CrushFTP lower than 10.5.1. Since then, the vulnerability has been tracked as CVE-2023-43177 and the security researchers at Converge published a blog sharing their findings on November 16. CVE-2023-43177 is a mass assignment vulnerability related to how CrushFTP parses request headers for the AS2 protocol. Successful exploitation could lead to unauthenticated, remote code execution (RCE).