Mailchimp
Not subscribed to OpsMatters Newsletter


The Payment Card Industry Security Standard Council (PCI SSC) for the benefit of customers, cardholders, and other stakeholders of the industry established a stringent payment card security standard known as PCI DSS. Payment Card Industry Data Security Standard is a framework designed and developed to protect sensitive card data in the environment. The payment security standard is a comprehensive framework that outlines 12 requirements that organizations are expected to meet to ensure compliance.
Threat actors are continuously honing their skills to find new ways to penetrate networks, disrupt business-critical systems and steal confidential data. In the early days of the internet, adversaries used file-based malware to carry out attacks, and it was relatively easy to stop them with signature-based defenses. Modern threat actors have a much wider variety of tactics, techniques and procedures (TTPs) at their disposal.
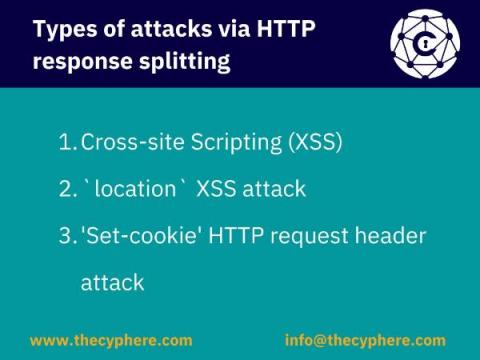
HTTP Response Splitting entails a kind of attack in which an attacker can fiddle with response headers that will be interpreted by the client. The attack is simple: an attacker passes malicious data to a vulnerable application, and the application includes the malicious data in the single HTTP response, thus leading a way to set arbitrary headers and embedding data according to the whims and wishes of the attacker.
The average company can’t do business without their third parties. Vendors, suppliers, partners, distributors, and contractors — third parties make it so much simpler to build, distribute and sell a product or service.