Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Latest posts

Navigating the FTC's Non-Compete Ban: A Guide for Information Security Teams

On April 23, 2024, the Federal Trade Commission (FTC) issued a ruling that banned the use and enforcement of non-compete agreements across the United States. With this ruling, enterprises that relied on these agreements to help preserve their competitive advantage must adapt their strategy for protecting proprietary information when an employee departs. Read on for a breakdown of the ruling, what strategies remain open for dealing with this risk, and how security teams can help their organization adapt.

Forward Networks named Great Place to Work in 2024 Fortune Best Workplaces in the Bay Area

Working in this industry means long hours and high expectations. At the same time, tech companies large and small in Silicon Valley are known for lavishing perks on employees; the bar for treating employees well is set high in the Bay Area.

Key Strategies for Preventing Downtime: The Role of Electrical Failure Analysis in Manufacturing

Have you ever wondered what goes on behind the scenes in the manufacturing industry when it comes to preventing costly downtime? In a world where efficiency is key, manufacturers are constantly striving to optimize their operations and minimize disruptions. One crucial aspect of this is electrical failure analysis, a process that delves deep into the root causes of electrical issues to identify and implement effective preventive measures.

Boost Your Site: Advanced WordPress Development Techniques

From that simple blogging tool to the advanced Content Management System running millions of websites today, WordPress has come a long way. The more popular it becomes, the greater the demand is for advanced development techniques that will set you apart amidst all the clutter in the digital landscape. We'll explore cutting-edge strategies that help take your WordPress site to the next level.

Elastic: LLM safety assessment: The definitive guide on avoiding and mitigating risks

For all the potential of GenAI, broad adoption has been guarded. This is because LLMs represent yet another potential entry point for malicious actors to gain access to private information or a foothold in an organisation's IT ecosystems. So how can you harness the full potential of GenAI without increasing the potential attack surface for cyber criminals to exploit? In this webinar, we'll unpick the findings from Elastic Security Labs' recent LLM Safety Assessment report.

Why outdated access control is putting your data at risk

Imagine this: you wake up to a notification – your company has suffered a data breach. Fear sets in as you think about what this means: customer data exposed, your company’s reputation damaged, and big fines on the horizon. In today’s digital landscape, this scenario is too common. Organizations worldwide face penalties for non-compliance with regulations, such as fines of up to $50,000 per incident for violating HIPAA.

Falcon Next-Gen SIEM Data Onboarding: Demo Drill Down

Start using your free 10GB/day of third-party data ingestion by learning how to onboard data with Falcon Next-Gen SIEM. Effortlessly accelerate third-party data ingestion with pre-built data connectors and out-of-the-box content - all within the CrowdStrike Falcon platform. Managing your data has never been easier with Falcon Next-Gen SIEM. CrowdStrike Falcon Next-Gen SIEM: Consolidate security operations with the world’s most complete AI-native SOC platform.

New usability enhancements make compliance easier than ever for startups

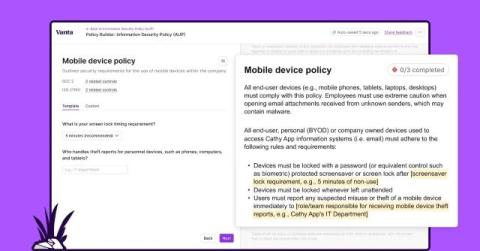
For startup leaders, getting compliant with common security and privacy frameworks, like SOC 2 and ISO 27001, is often necessary to unlock new revenue streams, expand upmarket, and prove trust. ‍ While there’s a clear need to get compliant, this process is often time-consuming, manual, and full of “one step forward, two steps back” moments.