Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Why Continuous Vulnerability Assessment Beats One-Time Scans for Real Security

Most organizations still treat vulnerability assessment (VA) as a checkbox activity, run a scan, generate a report, and move on. But security doesn’t work in isolated snapshots. Applications are dynamic, threats evolve by the hour, and even minor code changes can open new attack surfaces. This is where continuous vulnerability assessment (CVA) becomes essential.

10 Challenges in Vulnerability Assessments and How to Overcome Them Effectively

The 2025 Verizon DBIR reveals that vulnerability exploits now cause 34% more breaches than phishing. This makes vulnerability assessments essential for any security strategy. Yet many organizations struggle with incomplete scans, alert fatigue, and missed remediation, leaving critical gaps exposed. In this blog, we will explore the key challenges in vulnerability assessments and provide practical strategies to overcome them effectively.

5 Expenses MSPs Absorb without Web App & API Security

Uncover 5 major expenses Managed Service Providers (MSPs) often absorb when web application and API security isn't in place. From breach clean up cost to reputational damage, these hidden costs can impact your profitability and customer trust. Don’t let poor security planning hurt your bottom line. Watch now and learn how to eliminate these costs with a proactive security approach.

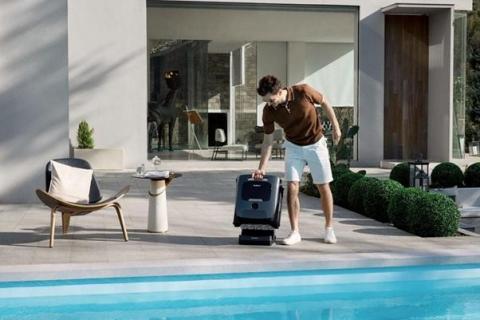
Top Cordless Robotic Pool Cleaners for 2025

It's easier than ever to keep your pool's water sparkling clean and clear without the hassle of scrubbingit by hand - thanks to the advent of therobot pool cleaner. Now, in 2025, the market place is awash with high performing cordless options that leave the old style, plug-inpool vacuums and skimmers for dead. Smart machines, including the newest pool robots, are engineered totackle anything from tiny particulates to stubborn algae-no cords, no hassle.

Humans at the Center: Redefining the Role of Developers in an AI-Powered Future

In a previous blog, we discussed how AI is reshaping software development at every level. This shift means developers need new skills to stay effective. In fact, Gartner predicts that generative AI will require 80% of the engineering workforce to upskill through 2027. So what can today’s developers do to stay ahead? Here are a few steps to consider.

What is an SBOM and Why is it Critical to Third-Party Risk Management?

A decade ago, the primary focus of TPRM was questionnaire management and distribution, usually done in a simple and manual way, relying on vendors to self-report on their security practices. Today the basic best practices of TPRM have grown to include continuous monitoring and other advanced AI-based capabilities like CVE alerting for third parties as elementary aspects of an effective program.