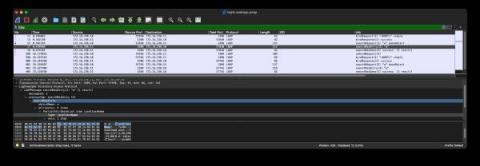
We recently discussed some methods for detecting the Log4j exploit, and we’ve now developed another method that everyone running Zeek® or a Corelight sensor can use. Our new approach is based on the rarity of legitimate downloads of Java via LDAP. Zeek does not currently have a native LDAP protocol analyzer (though one is available if you are running Spicy). This will not stop you from detecting this exploit downloading Java over LDAP, though. To see how, read on.
In quick succession in December, The Apache Software Foundation released information on two critical vulnerabilities in its Log4j Java-based library. The first vulnerability CVE-2021-44228, also known as Log4Shell or LogJam, was reported as an unauthenticated remote code execution (RCE) vulnerability. By exploiting how the library logs error messages, it could lead to a complete system takeover.
The United States Department of Homeland Security (DHS) is inviting security researchers to uncover vulnerabilities and hack into its systems, in an attempt to better protect itself from malicious attacks.
When it comes to cybersecurity governance and management, there is no “one size fits all” approach. Today’s CISOs have a far wider range of responsibilities than their predecessors as heads of IT security. The CISO role is no longer purely technical, focused on hardware and endpoint protection and on operations within the organisational perimeter. Today’s CISO is as likely to be involved with software security, cloud applications, security awareness, and user training.