Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

What we learned at KubeCon + CloudNativeCon Europe 2022: From presentations to accolades

It was a busy week last week at KubeCon +CloudNativeCon Europe 2022 in Valencia, Spain. It seemed like the entire world related to Kubernetes came together after two years of being apart. It was fulfilling meeting up with our peers and gaining market insight- face-to-face. Catalogic’s core messaging this year has revolved around cyber-resilience for data protection.

Introducing our brand new (and free!) Calico Azure Course

Calico Open Source is an industry standard for container security and networking that offers high-performance cloud-native scalability and supports Kubernetes workloads, non-Kubernetes workloads, and legacy workloads. Created and maintained by Tigera, Calico Open Source offers a wide range of support for your choice of data plane whether it’s Windows, eBPF, Linux, or VPP. We’re excited to announce our new certification course for Azure, Certified Calico Operator: Azure Expert!

Shift left is only part of secure software delivery

We’re living in the age of accelerated consumption and delivery. You can get a seemingly infinite selection of products delivered to your door within two days, for free, from thousands of miles away. You can access an endless variety of services online within mere seconds: Movies, music, games, education and even health care. These modern marvels are afforded to us by relatively recent advances in software development, delivery and operations.

Mitigating controls for cloud-native applications: Why you need them and how Calico Cloud can help

Fixing vulnerabilities can be hard—especially so for cloud-native applications. Let’s take a deeper look at why this is, and how mitigating controls can help secure your cloud-native applications.

Trends at Blackhat Asia 2022 - Kubernetes, Cloud Security and more

This week BlackHat Asia 2022 took place in hybrid mode. It’s one of the most important events within the #infosec community, where security experts show how far they can go. In this edition, the trend of talks and tools focused on improving the security of Kubernetes, Cloud Security or Supply Chain, either from the perspective of the blue team or the red team.

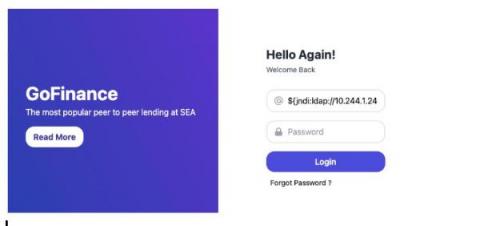
Spotting Log4j traffic in Kubernetes environments

Editor’s note: This is the latest in a series of posts we have planned over the next several weeks where we explore topics such as network monitoring in Kubernetes, using sidecars to sniff and tunnel traffic, show a real-world example of detecting malicious traffic between containers, and more! Please subscribe to the blog, or come back for more each week.

How to get a shell in a Kubernetes Pod

Containers are used for packaging software and all its dependencies before deployment. Before the era of containers, software developers had to deal with compatibility issues during deployment. These could occur when software functions properly during the development phase but fails to function due to dependency issues in the production environment. With containers, however, all the software dependencies used for development can be shipped and used in the production environment.