Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

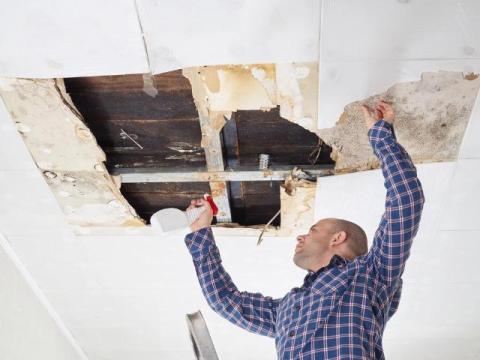
How Rapid Mitigation Prevents Structural Rot During Water Damage Cleanup in Baltimore, MD

After a heavy rainstorm or a burst pipe, Baltimore homeowners often face the urgent challenge of water seeping into basements, crawl spaces, and behind walls. Left unchecked, this moisture quickly becomes more than a cosmetic issue-wood beams, subfloors, and wall studs can begin to deteriorate, threatening the structural safety of the entire building. Rapid mitigation, meaning immediate intervention to remove water and dry affected areas, is the most effective way to halt the progression of rot and mold.
Coral Way Residential Properties: Essential Seasonal Checklist for Scheduling Leak Detection and Repair in Miami, FL

Homeowners in Coral Way, Miami, often encounter unique challenges with plumbing due to the region's subtropical climate. Sudden heavy rainfalls in spring and summer, combined with high humidity and aging infrastructure in many properties, can increase the risk of hidden water leaks. Residents may notice unexplained increases in their water bills or damp spots on walls after a storm, prompting concern about potential damage behind the scenes. Addressing these issues promptly helps prevent structural problems, mold growth, and unnecessary expenses.

5 Patch Manager Plus settings to configure before Exploit Wednesday

Patch Tuesday gives IT teams fixes. It also gives attackers a map. When Microsoft publishes its monthly security updates, researchers and threat actors alike can compare patched and unpatched files to pinpoint exactly what was broken. The day after, informally known as Exploit Wednesday, is when working exploits for freshly disclosed flaws start to circulate. Every endpoint that's still unpatched is now a documented target.

Reach Security Recognized as a CRN® 2026 Stellar Startup

San Francisco, CA, November 9, 2026 - Reach Security, the AI that operates security defenses at machine speed, today announced that CRN , a brand of The Channel Company, has included Reach Security on its 2026 Stellar Startups list in the Security category for a second year in a row. This prestigious list highlights fast-rising technology vendors that are driving innovation and fostering growth in the IT channel with groundbreaking products.

How to Evaluate a Shadow AI Detection Tool in a Trial

A shadow AI detection trial produces a number within days. The tool reports how many AI applications it discovered, and the number is usually larger than anyone expected, which feels like proof that it works. ‍ It is not. Every tool in this category reports what it found. None of them reports what it missed, and the thing a buyer needs to know is the size of the second number. ‍

AI Vendor Questions, and How to Check the Answers

Most security teams now run an AI-specific questionnaire alongside the standard one, often forty to sixty questions long, and the lists have converged. Training on customer data, retention, subprocessors, model provenance, human oversight, logging, incident response. ‍ Having the list is no longer the hard part. Every answer arrives as a sentence from the vendor, and a sentence is not evidence. ‍

Trust Alone Is No Longer a Security Control

For years, cybersecurity awareness training has focused on helping employees identify suspicious communications. Check the sender, look for mistakes, question unusual requests. But artificial intelligence is changing the rules. Today, cybercriminals can generate convincing emails, clone voices, and impersonate trusted individuals with unprecedented accuracy. The challenge is no longer spotting obvious scams. It's recognizing that many malicious communications may appear completely legitimate.

How does Aurora Adaptive Threat Protection stop advanced cyber threats?

Aurora Adaptive Threat Protection in Action: Stopping Ransomware Before the Damage Is Done What happens when a user clicks a malicious file that bypasses traditional defenses? In this demo, you'll see how Arctic Wolf Aurora Adaptive Threat Protection uses AI-powered, intent-based detection to identify and disrupt ransomware activity in real time, stopping attacks before encryption can spread across the environment.

Report: Social Engineering Remained the Top Initial Access Vector in Q3 2026

Phishing remained the most common initial access vector for attackers in the third quarter of 2026, according to a new report from Cisco Talos. Ransomware gangs are using voice phishing attacks to trick employees into granting them a foothold within organizations.