Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

FIPS 140 2 End of Life: Impact on HSMs and Cryptographic Modules

The shift from the FIPS 140-2 standard is significant for organizations making use of HSMs, software-based cryptographic modules, VPN equipment, secure communications, and other items depending on validated crypto. That being said, it does not mean that the existing FIPS 140-2 modules will start malfunctioning or will become insecure. The transition has implications for how businesses will be appraising validated crypto devices, especially when purchasing or employing them in the new systems.
Zenity for Claude Tag: Securing the Shared Agent in Your Slack Workspace

Your team just hired someone who never sleeps, reads everything, and takes work from whoever asks. That’s the elevator pitch for Claude Tag, and on the face of it, it’s hard to see why anyone would push back on the new hire. Enterprises will want this in every workspace. On-demand status updates, first drafts, streamlined triage; the work that quietly eats a week now collapses into the team conversation.

Meet Dai Fujimoto: Building Zenity's Next Chapter in Japan

Japan’s Ministry of Finance reports that AI adoption in large local enterprises has surged to 89%. Companies are progressively choosing to incorporate AI agents into their workflows, building with Microsoft Copilot Studio, ChatGPT Enterprise, Claude, and a myriad of other platforms, all living across a variety of environments with autonomy, privilege, and minimal supervision.

Your AI Transformation Needs Runtime Protection for the Whole Agentic Estate

AI Detection and Response (AI-DR), also called AI runtime security, is quickly becoming a must-have. Prompt injection, jailbreaks, and data leakage are real, and the prompt is often where attacks begin. But the prompt is only the first hop. In an agentic enterprise, a single instruction can trigger activity well beyond the LLM, all the way to your business systems and data.

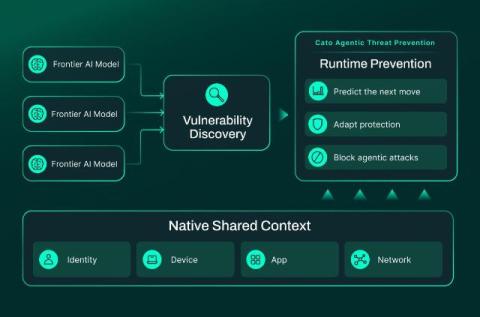
Beyond Model Access: Frontier AI Defense Needs Runtime Prevention

Access to powerful AI models is opening new possibilities for cybersecurity. Models can help uncover weaknesses, investigate threats, and explore how attackers might break into an environment. Using several models can bring different strengths to that work. But model access alone does not answer a critical question: can your defense stop an attack while it is happening? In the frontier AI era, discovery needs to connect to action.

Wait, Did We Just Invent Classifiers Again? Introducing Jev, a new way to do AI.

For the last few years, when somebody says “AI,” what they are usually referring to is a Large Language Model, or LLM for short. You chuck some text in, it has a think, and it gives you some more text back. This is brilliant if you want code written, documents summarised, or quantum physics explained to you in a limerick, but while this is great for humans, most software doesn’t actually want a beautifully written paragraph. Software just wants an answer so it can make a decision.

How to Build the Business Case for ASPM Software

Start with what the current backlog already costs: analyst hours spent on triage, developer time lost to duplicate tickets, slow MTTR, and manual reporting. Then tie each benefit of ASPM software to one of those costs, such as fewer tickets per fix or faster remediation. Compare pricing models on your real numbers, including integration upkeep, and propose a measurable pilot on five to ten high-value applications. Most AppSec teams don’t need to be sold on ASPM software.