Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The latest News and Information on Security Incident and Event Management.

Sponsored Post

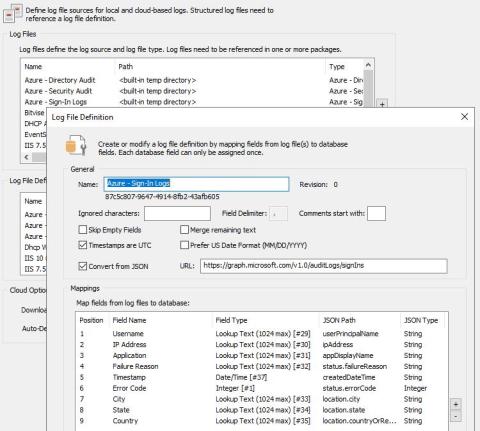
EventSentry v6: Azure Logs, HEC, Sigma, Log Signing & More

Even though the shift to the cloud has slowed recently as many businesses are moving certain workloads back on-premise, Microsoft Exchange remains one cloud-based service that most organizations continue to embrace – despite its frequent outages. This doesn’t come as a surprise, as Microsoft has successfully devolved on-prem Exchange Server – the only viable alternative – into an unfriendly dragon that even experienced sysadmins won’t touch with a 10 ft pole.
Token Torching: How I'd burn your AI budget (so you can fix it)

I spend most of my time thinking like a criminal. Not because I’m edgy, but because that’s literally the job. And lately, everywhere I look, I see the same thing: People are exposing MCP endpoints like they’re REST APIs, and forgetting they’re actually money execution engines. So let’s talk about Token Torching. Yes, I invented another name. This isn’t data theft. It’s not taking your service down.

SIEM Automation to Improve Threat Detection and Incident Response

Security professionals often compare their jobs to a game of “Whack-a-Mole,” the arcade game where players try to hit little plastic moles on the head. The moles pop up in a randomly generated way, making it difficult to predict which one will show its little head next.

Top 10 SIEM best practices for modern security operations

Nowadays, it’s not uncommon for enterprise IT leaders to find themselves in a situation that seems like a catch-22. On one hand, they’re expected to make data-driven decisions that improve productivity and profitability in a business. On the other, they’re preoccupied with their core responsibilities such as protecting critical systems, maintaining network security, and accelerating investigations when a security event occurs. Traditional tooling won’t keep up with modern systems.

Decoding the 2025 MITRE ATT&CK Evals: A Call for Clarity and a Guide for Analysts

The latest MITRE ATT&CK Enterprise Evaluations are out, featuring scenarios that emulate sophisticated actors like Scattered Spider and Mustang Panda. While every release of the findings is a significant event for the security community, this year’s evaluation highlights both new and recurring concerns for security professionals.

Using LLMs, CVSS, and SIEM Data for Runtime Risk Prioritization

A recent University of North Carolina Wilmington study tested whether general-purpose large language models could infer CVSS v3.1 base metrics using only CVE description text, across more than 31,000 vulnerabilities. The results show measurable progress, but they also expose a hard limit that matters far more than model selection: Model quality helps, but missing context sets a ceiling on reliability.

PGA of America Trusts LevelBlue as Official Cybersecurity Advisor

LevelBlue and the PGA of America share a commitment to excellence under pressure. As the Official Cybersecurity Advisor of the PGA of America, LevelBlue brings championship standards of protection, continuity, and trust to the organizations that keep the game - and business - moving forward. From fairways to firewalls, LevelBlue safeguards mission-critical operations, member data, and high-profile events with always-on defense, accelerated response, and expert-led security operations powered by AI-driven threat intelligence.