Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Selling to the Government? Here's What CMMC Means for You

CMMC Phase 2 enforcement lands in November 2026, and C3PAOs are already warning about assessment capacity. If your configuration management domain isn't audit-ready, this is the walkthrough to fix that. Roy Ludmir breaks down what changed in enforced CMMC as of November 2025, what auditors actually test versus what they just ask about, and where most organizations get stuck below full compliance — plus which security baselines to standardize on and how to build an evidence package that holds up under a real assessment.

AI Just Shrank the Time Hackers Need to Weaponize Your Vulnerabilities

The Five Eyes intelligence alliance—NSA, CISA, GCHQ, Australia's ASD, Canada's Cyber Centre, and New Zealand's GCSB—just issued a joint warning: AI has compressed the window between vulnerability discovery and exploitation from years to months. Adrian breaks down what the "AI Shift in Cyber Risk" statement actually means for patching timelines and attacker sophistication—and why most organizations aren't moving fast enough to keep up.

Ep. 65 - "Months, Not Years": The Five Eyes AI Warning and Your Security Program

On June 22, 2026, the heads of all six Five Eyes cyber agencies—GCHQ, CISA, the NSA, ASD, the Canadian Centre, and New Zealand's GCSB—signed a rare joint statement: AI has rewritten the cyber risk timeline, and it's months, not years. Host Tova Dvorin and offensive security expert Adrian Culley unpack why AI is collapsing the window between vulnerability and exploit, why "having controls" isn't the same as proven controls, and why legacy systems are now strategic liabilities for the board, not the IT team. A clear-eyed look at validation, assumed breach, and what CISOs should do Monday morning.


Alex Stamos has 23 minutes to stop an AI chatbot leaking data (Live Tabletop Exercise)

What does a security leader actually do when an AI chatbot starts confidently revealing customer data that was never supposed to see the light of day? Alex has spent his career at the intersection of security and the hardest problems in tech—Chief Security Officer at Yahoo, Facebook, and SentinelOne, founder of the Stanford Internet Observatory, and now Chief Product Officer at Corridor, a startup focused on the security and safety of AI coding agents. If anyone knows what it looks like when AI ships faster than security can keep up, it’s him.

Episode 2: Least privilege access

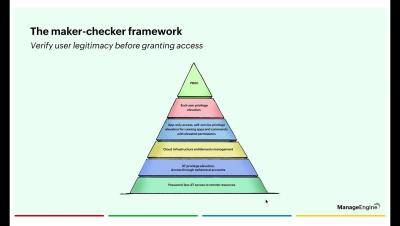
In this episode, we'll walk you through one of the core tenets of PAM360: eliminating standing privileges. You will learn how to replace permanent administrative access with just-in-time (JIT) privilege elevation, reduce your attack surface, and enforce least-privilege access across your endpoints and critical systems. We will also break down PAM360's privilege elevation framework—built on a maker-checker model and policy-based access—so you can configure and scrutinize access requests, automate approvals, and enable dynamic controls for applications and user actions.

Optimize Microsoft Entra ID Conditional Access | Reach Security

Which of your users can reach a sensitive app without ever hitting MFA? Most security teams can't answer that with confidence. Microsoft Entra ID and Conditional Access is powerful. But exclusions stack up, MFA coverage drifts, and risk-based protections go unused. This creates openings for fast-moving AI-powered attackers. Reach continuously validates your controls against your security intent, closes the gaps, and proves the risk reduction.