Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

CIPA for websites in 2027: what the law still covers, and how to show what your site does

If people in California use your website or app, assume CIPA applies. CIPA was written for telephone wiretapping, and courts have applied its "technology-neutral" terms to online communications for years. The business's location does not matter; the visitor's does.
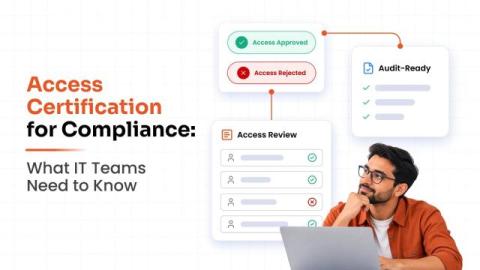
Access Certification For Compliance: What IT Teams Need To Know

An access review can look complete on paper. The campaign closed, reviewers made their decisions, and the records were saved. Then an auditor asks: Who reviewed this access, what did they decide, and what happened afterward? That question can reveal problems that a completed review does not show. A rejected permission may still be active. An exception may have no clear reason. The team may also struggle to show when the review happened.

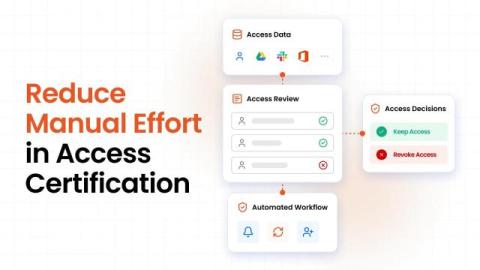
How to Reduce Manual Effort in Access Certification

Access certification can take more time than the actual review. A manager may need to review access for 50 employees. Before that happens, someone has to gather the access data, identify the right reviewer, send the requests, and track the responses. If the reviewer revokes access, someone may also need to remove it from the application. Now repeat that across hundreds of users and several applications. The workload adds up quickly.

Under CPS 234, Your APIs Are Information Assets. Can You Prove You're Protecting Them?

APRA's information security standard already covers the APIs your agents run on. Most institutions cannot yet evidence it. All APRA-regulated institutions in Australia are bound to meet CPS 234. This is the Prudential Standard for Information Security. Whether that's a bank, insurance provider, or super fund, they all fall under CPS 234, as do their third-party providers. Together, these institutions hold trillions of dollars in assets.

CISO Risk Intel Brief: Record Patch Volume, Edge Zero-Days, and AI-Accelerated Supply Chain Pressure

This briefing examines material developments across the most recent seven-day period and the preceding thirty days. It is written for executive and board consumption and focuses on residual risk, control effectiveness, material exposure, and the practical implications for application security programs, software supply chain integrity, edge and identity systems, and the accelerating role of AI in both attack and defense.

Acronis expands MDR toward broader workspace protection

Cyberattacks do not respect normal business hours: They can happen at night, on weekends and during holidays. Acronis MDR by Acronis TRU gives partners 24/7/365 expert monitoring, investigation and response without having to build their own security operations center (SOC). Acronis is expanding the MDR service with capabilities that make this expertise easier to deliver and help partners address more risks. The developments build on a broader commitment to managed security.

Apono Brings Just-in-Time Access to AWS IAM Account Access Manager

AWS just shipped AWS IAM Account Access Manager (AAM), a new way to grant AWS access through AWS IAM Identity Center using IAM roles. Apono is supporting AAM from day one, bringing just-in-time provisioning directly to the IAM roles your teams already trust. If you’re running AWS IAM Identity Center today, you’re likely provisioning access through permission sets.

Why Choose Exabeam Over QRadar and Cortex XSIAM for SIEM?

Exabeam delivers stronger detection, faster investigations, and more flexible deployment than IBM QRadar and Cortex XSIAM. It combines user and entity behavior analytics (UEBA), Agent Behavior Analytics (ABA), and agentic AI through Exabeam Nova AI to reduce alert noise and automate workflows. With cloud-native capabilities in New-Scale Fusion, Exabeam gives security teams a modern approach to SIEM and security operations.

Why CISOs Need an Agentic SOC Strategy

CISOs need an agentic SOC strategy because traditional staffing models can’t scale to match machine-speed threats, a global talent shortage, and rising alert volume. An agentic SOC pairs AI agents that collect evidence and investigate at machine speed with analysts who provide judgment, context, and accountability. Exabeam combines Agent Behavior Analytics (ABA), Exabeam Nova AI, and automated investigation to expand coverage and speed response without adding headcount.