Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Board Foot Calculator Apps for Android

This is a working comparison of five Android options, written for people who bid, order, and take delivery on lumber for a living. No formula refresher, no explanation of what a quarter is. The question here is narrower: which board foot calculator app for android holds up when the tape says 6' 2-13/16", the crew is waiting, and a rounding error becomes a short order or a return trip.
Cloud Computing Security for Community Organizations: Protecting Sensitive Data

Church work today runs through shared drives, livestreaming platforms, donation portals, email accounts, volunteer databases, and pastoral care systems. That shift happened gradually, often without a formal security plan. One tool arrived for scheduling, and another handled giving. At the same time, someone created a spreadsheet for member details. Before long, sensitive information sat across several cloud services, managed by staff and volunteers with very different technical skills.

How to Protect Digital Ministries in the Age of Cloud Computing

Church ministry no longer stops at the sanctuary door. Livestreams, online giving, prayer forms, volunteer platforms, email systems, and social channels now carry much of the weekly work. That reach is certainly important. But still, every new account creates another place where credentials, personal records, or payment information can slip into the wrong hands. Churches often manage this digital estate with small teams, rotating volunteers, and limited technical oversight.

The Truth About Server Rentals!

Imagine you have just bought a brand-new Ferrari. It is sleek, ridiculously fast, and smells like success. Now imagine trying to squeeze that engineering masterpiece into a cramped, shared communal garage with fifty neighbors who park their broken minivans inches from your doors, leave open paint cans lying around, and occasionally block the exit for hours. Sounds completely insane, right? Yet every single day, thousands of smart, growing businesses make this exact mistake with their digital infrastructure.

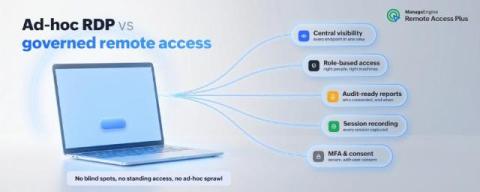
Why unmanaged RDP is risky at enterprise scale (and how to regain control)

Remote Desktop Protocol (RDP) is the path of least resistance for gaining access to another Windows machine. It is built into the OS, it is free, and almost every admin and help desk technician already knows how to fire up mstsc.exe and type in a hostname-as simple as that. That convenience is exactly why RDP is everywhere inside corporate networks.

Closing the Gap: What Actually Turns Agent Telemetry Into Evidence

‍ An AI coding agent's own telemetry answers real questions well: which agents are running, what they invoked, the shape of a session, whether a run looks abnormal. It cannot, no matter how completely it is instrumented, stand alone as evidence. The agent under review is also the party writing the record. The record shows an attempt, not an outcome. And the vocabulary for describing any of it is still being written in public, one unstable commit at a time.

ASM Has a Silent C, and It Stands for Change Management

If you run a security team, a large part of the job is responding to change. Something in the environment moves, and you have to work out whether risk moved with it, and how quickly you need to act. Those changes arrive from two different directions, external and internal. Of course, we’re all familiar with the external ones. A new CVE drops, a proof of concept goes public, a ransomware group starts naming your sector. The internal ones start inside your own organization.

Pikabot Malware: Delivery Methods, Evasion, and Impact

Originating in early 2023, Pikabot emerged as a significant malware loader. Over the past year, ThreatLabz has diligently monitored its development and operational methods. Notably, there was a surge in Pikabot’s usage in the latter part of 2023, attributed to a BlackBasta ransomware affiliate adopting Pikabot post the FBI-led Qakbot takedown. However, Pikabot’s activity ceased shortly after Christmas 2023, with version 1.1.19 marking its endpoint.

Mini Shai-Hulud hits openapi-react-query-codegen: 10 malicious npm versions

On August 28, 2026, ten malicious versions of @7nohe/openapi-react-query-codegen were published to npm between 20:00 and 20:21 UTC. The package generates React Query hooks from an OpenAPI schema and draws roughly 150,000 weekly downloads. The latest tag pointed at the malicious 3.0.4 for the duration of the window. Eight of the ten releases carry a multi-stage loader that reaches for cloud, registry, and developer credentials. The attacker needed no stolen npm token and no hijacked maintainer account.

How to Do Prompt Injection Testing on an Agent in Under Ten Tests

A prompt injection test suite can only report on the payloads it contains. That sentence is the whole problem with the number most teams have. Somewhere in a ticket there is a scan result: a scanner threw several hundred probes at the endpoint and a percentage got through. The percentage is real.