Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Endpoint Protector picks up 8 G2 badges for Fall 2026

Netwrix Endpoint Protector earned 8 G2 badges in the Fall 2026 reports, including Leader recognition in Data Loss Prevention (DLP) and Data Security, plus Regional Leader and High Performer badges across multiple regions. Endpoint Protector holds a 4.5 out of 5 rating from more than 160 G2 reviews, driven by feedback on fast support, quick implementation, and consistent policy enforcement. Buyers evaluating DLP tools have to take a lot on faith.
Best practices: How to implement Kerberos authentication correctly in your AD environment

Authentication configuration issues, especially those tying into Kerberos, are a big call driver for the Active Roles by One Identity Support team. When Kerberos requirements are met, Integrated Windows Authentication typically attempts Kerberos before falling back to NTLM. Due to expected IIS functionality, we will see multiple HTTP requests which trigger authentication repeatedly.

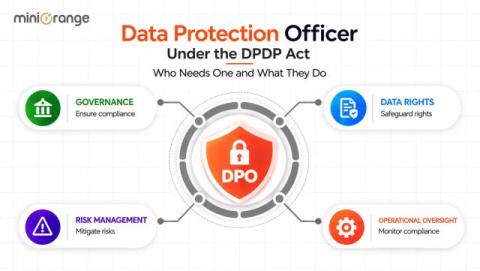
Data Protection Officer Under the DPDP Act: Who Needs One and What They Do

Not every organization that processes personal data has to appoint a Data Protection Officer. Under India's Digital Personal Data Protection Act, 2023, this duty applies only to Significant Data Fiduciaries (SDFs), a category the government assigns based on the scale and sensitivity of the data an entity handles. So before you assume your business needs a data protection officer, it helps to know exactly where this obligation begins and ends.

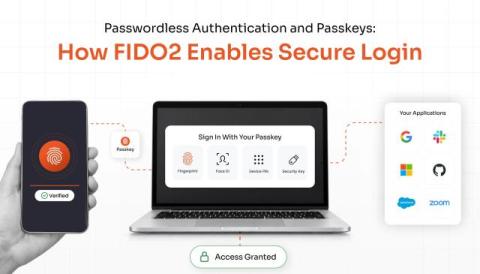
Passwordless Authentication and Passkeys: How FIDO2 Enables Secure Login

Password-based authentication is slowly disappearing from the login experience in 2026. Instead, users increasingly authenticate with a fingerprint, device PIN, or security key without typing a password. This is where passwordless authentication and passkeys come in. Built on FIDO2 and WebAuthn, passkeys use cryptographic credentials to make passwordless login simpler for users while reducing exposure to phishing and credential theft. But passkeys are only one part of the picture.

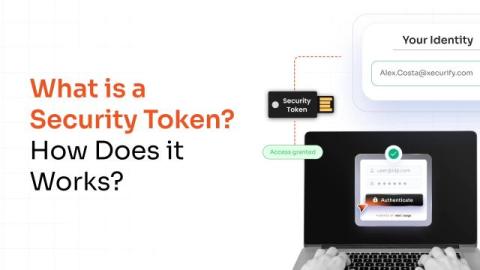
What Is a Security Token? How Does It Work?

A security token is a physical device, digital object, or software credential that helps verify a user's identity before granting access to a system, application, network, or account. Depending on the type, it can generate a one-time password (OTP), store cryptographic credentials, or work with an authentication system to prove that the person requesting access possesses the authorized token.

"Better than the tools we were quoted six figures for": How Tines' finance team built a custom billing app for <$1,000

At Tines, Salesforce and NetSuite form our core finance and billing stack. But anyone using these tools will be familiar with the issues this set-up presents — it requires manual, time-consuming work to connect data across the two platforms. Over the years, my team evaluated a bunch of solutions to this problem, including third-party tools and NetSuite’s own native offering.

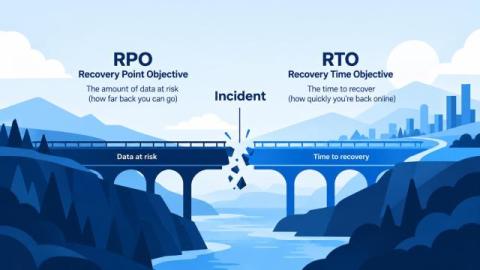
RTO vs RPO: What They Mean and How to Set Them Honestly

Recovery time objective (RTO) is how long a system can be down before the impact becomes unacceptable. Recovery point objective (RPO) is how much data the business can afford to lose, measured as a window of time before the incident. RTO looks forward from the moment things break. RPO looks backward from it. That distinction takes a paragraph to explain and years to get right, because the difficult part was never the definition.

Millions of Phishing Emails Use ASCII Smuggling to Bypass Security Filters

A massive phishing campaign is using invisible Unicode tag characters to evade security filters, according to researchers at Microsoft. This technique, known as “ASCII smuggling,” has grown popular over the past year for launching AI prompt injection attacks, but the same tactic can hide suspicious text in emails.

The New Agent Control Standard Names the Controls, Not Their Value

The OWASP GenAI Security Project unveiled an Agent Control Standard in early September, donated to the project and aimed at runtime enforcement for agentic systems. It sets out that agents should be inspectable, traceable and instrumentable, with declarative hooks and policy enforcement across frameworks. ‍ It answers which controls belong around an agent.

Why AI Review Cannot Keep Up With the Decision

That human review becomes a bottleneck as agents scale is now widely observed. Five or ten agents working in parallel produce more decisions than one reviewer can evaluate, and under queue pressure the review degrades into approval without examination. ‍ The usual response is to move up a level, reviewing intents and boundaries rather than individual outputs.