Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Mend.io upgrades 184 open source organizations to the Renovate Community (OSS) plan

Mend.io has proactively upgraded 184 open source organizations and GitHub users to the Mend Renovate Community (OSS) plan, with no request required. The upgrade covers about 3,000 repositories with roughly 4 million combined GitHub stars. Maintainers get higher resource limits, more concurrency, and access to Merge Confidence.
NIST SSDF: 4 core practices for secure software development

The NIST Secure Software Development Framework (SSDF) is a set of fundamental, outcome-based practices that integrate security throughout the software development lifecycle (SDLC). Documented in NIST SP 800-218, it helps organizations reduce vulnerabilities, prevent recurrences, and establish a common language for secure development. The SSDF outlines dozens of tasks grouped into four high-level categories.

What Is AI Governance? A Practical Framework for Security Teams

The speed of AI integration is rapidly outpacing corporate governance capabilities. Generative AI is now embedded in development workflows and business applications, while agentic AI can make decisions and take actions with limited human intervention. That governance gap is becoming harder to ignore. Gartner predicts that more than 40% of agentic AI projects will be canceled by the end of 2027 because of escalating costs, unclear business value, or inadequate risk controls.

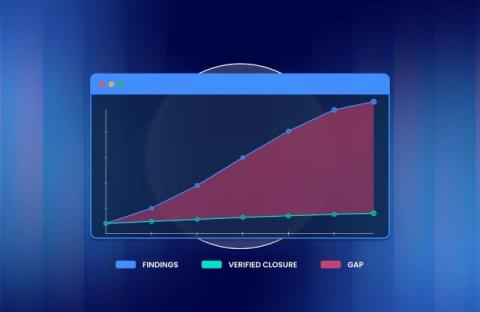
Detection scaled. The loop did not.

Findings got cheap. Verified closure did not. That AppSec remediation gap is the actual problem. AppSec spent a decade winning the wrong race. We got very good at finding things. Scanners in CI. SCA on every manifest. SAST on every pull request. Container and IaC checks on the way to the cluster. Then AI arrived and did what AI does to a solved problem: it made discovery cheaper, louder, and continuous. The same model that writes the function will also enumerate the ways to break it.

Mend Renovate Enterprise: managing dependencies at agentic scale

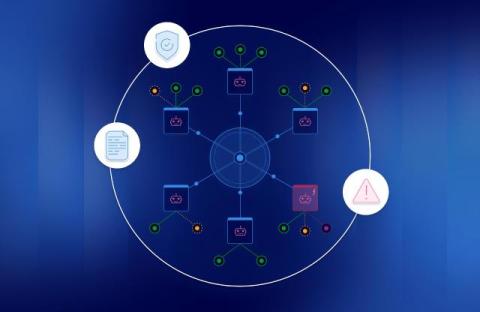
Automated dependency updates are not new. For years, Mend Renovate has scanned repositories, flagged outdated or vulnerable packages, and opened pull requests. What has changed is the sheer velocity of the pipeline. AI coding agents now write a significant share of production code, introducing open source packages continuously across thousands of repositories.

Mini Shai-Hulud hits openapi-react-query-codegen: 10 malicious npm versions

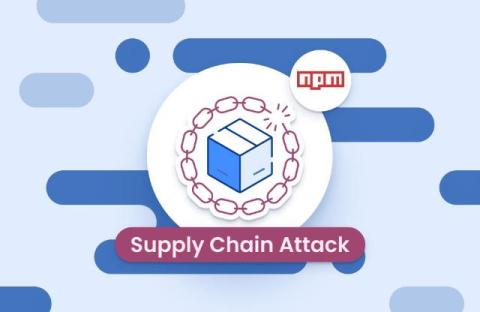
On August 28, 2026, ten malicious versions of @7nohe/openapi-react-query-codegen were published to npm between 20:00 and 20:21 UTC. The package generates React Query hooks from an OpenAPI schema and draws roughly 150,000 weekly downloads. The latest tag pointed at the malicious 3.0.4 for the duration of the window. Eight of the ten releases carry a multi-stage loader that reaches for cloud, registry, and developer credentials. The attacker needed no stolen npm token and no hijacked maintainer account.

The skill layer is a dependency problem without a lockfile: what the OWASP Agentic Skills Top 10 gets right

OWASP published version 1.0 of the Agentic Skills Top 10 on August 17, defining ten risk classes for the layer where agents find, load, and run reusable instructions and code. This standard arrived while the problem was still forming, mapping directly to AISVS, the Agentic Security Initiative Top 10, the MCP Top 10, ISO/IEC 42001, and the NIST AI RMF. It ships with working code for signing, sandboxing, and pinning.

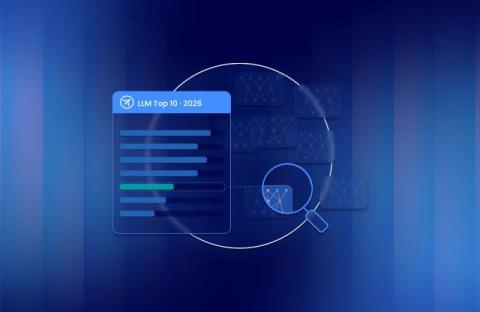
OWASP LLM Top 10 2026: the model will be fooled, the question is what breaks

The OWASP GenAI Security Project published the 2026 edition of its Top 10 for LLM Applications. Prompt Injection stayed at number one. Sensitive Information Disclosure stayed at number two. Read the headlines and you would conclude that not much moved. Something did move, and it is not in the rankings. The project leads open by telling you to stop trying to build a model that cannot be fooled, and to build the system around it so that when the model is fooled, nothing important breaks.

EU AI Act: risk tiers, timeline, and compliance requirements

The EU AI Act is a regulatory framework governing the development, deployment, and use of artificial intelligence within the European Union. The European Commission proposed it to keep AI systems placed on the EU market safe and transparent and to make sure they respect fundamental rights. The Act sets obligations for AI providers, users, and other stakeholders to address risks associated with AI while still supporting innovation and investment in the sector.

That's a wrap: Mend.io at Black Hat USA 2026

Another Black Hat USA is in the books, and what a week it was. From a main stage keynote at the AI Summit to candid podcast conversations, a video interview with Cyber Defense Magazine, and a booth game that just wouldn’t quit, Mend.io showed up in Las Vegas ready to talk about the question every security leader is wrestling with right now: as AI reshapes both the software we ship and the systems we have to defend, who do we trust to verify that it’s safe?