Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

WatchGuard MITRE ER7 Insights: Full Visibility, Prevention & Zero Friction

Every year, security teams and MSPs look to the MITRE ATT&CK Evaluations for one thing: clarity. Not marketing, but a transparent view of how endpoint products behave under real adversary tactics. MITRE ATT&CK Evaluations Enterprise Round 7 (MITRE ER7) is no exception. In the Windows “Hermes” scenario, modeled after Mustang Panda activity, the data shows how WatchGuard delivers strong, reliable protection with lower operational burden for security teams and MSPs.

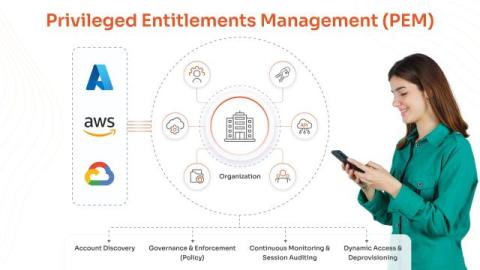
Privileged Entitlements Management (PEM): A Complete Guide

Privileged Entitlements Management (PEM) is a specialized cybersecurity practice that focuses on securely managing high-risk entitlements, also known as permissions, access rights, or privileges, which grant access to sensitive data, critical resources, and essential services across an organization's IT infrastructure.

Cato CTRL Threat Brief: "React2Shell" Vulnerability Targeting React Server Components

On Wednesday, December 3, a critical remote code execution (RCE) vulnerability in React Server Components (RSC), dubbed React2Shell (CVE-2025-55182), was disclosed. The CVE was discovered by security researcher Lachlan Davidson. It quickly gained traction with multiple third-party proof of concepts (PoCs) being published of varying quality and credibility.

The Resurgence of Mirai: Jackskid Botnet and Escalating IoT Threats in November 2025

The Mirai botnet, first unleashed in 2016, continues to evolve into increasingly sophisticated variants, posing severe risks to the Internet of Things(IoT) ecosystem. This report examines the Jackskid Botnet—a newly identified Mirai derivative—characterized by its aggressive propagation via zero-day exploits and brute-force attacks, resulting in daily active bot IPs surpassing 40,000 as of late November 2025.

Top Trends in Deception Technology: Predictions for 2026

Attackers thrive on ambiguity. They blend into normal traffic, pivot between cloud and on-prem systems, and use valid credentials to move quietly. Your conventional controls—while essential—often fire only after risky actions are taken on real assets. Cyber deception flips that sequence: it places deception decoys, breadcrumbs, and fake assets in the attacker’s path so that any touch is a high-fidelity signal.

CVE-2025-55182: The critical React RCE and the hidden risk in your supply chain

‍On December 3rd, the React team disclosed a critical security flaw in React Server Components known as CVE-2025-55182. With a CVSS score of 10.0, this issue is extremely severe. React and Next.js are the backbone of the modern web. Consequently, this vulnerability likely sits deep within your third-party vendor ecosystem in addition to your own codebase.

AI Browsers Are Here-But Enterprises Aren't Ready. Why Obrela Advises Extreme Caution

The cybersecurity landscape is changing at a pace we haven’t experienced since the dawn of cloud computing. The newest disruptor, the rise of AI browsers such as Perplexity Comet and OpenAI’s ChatGPT Atlas, promises to revolutionize user interaction with the web. But behind the innovation lies a long list of risks that enterprises cannot afford to ignore.

AI at the inflection point: Reclaiming human creativity and productivity

Artificial intelligence is changing how businesses work and compete. In every corner of the market, organizations expect more productivity. The question facing today’s business leaders is no longer whether to embrace artificial intelligence but how to harness its full potential to drive meaningful and sustainable transformation.

How RBAC Simplifies Active Directory Delegation and Strengthens AD Security

An IT helpdesk handling access requests all day is not unusual. A Finance hire waits for folder access because it has to be added manually. A contractor’s permissions stay active weeks after their project ends because no one tracks every group they were added to. These small gaps turn into bigger security risks when the environment grows. This happens when Active Directory permissions depend on individual updates and scattered delegation. Access becomes inconsistent.