Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

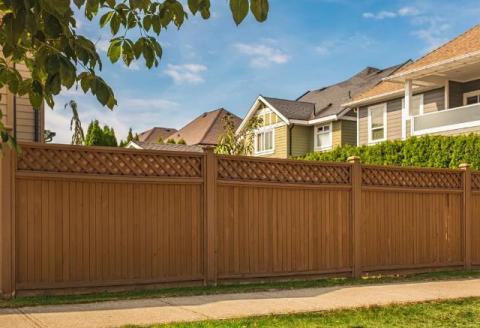
Fence Maintenance Tips to Keep Your Calgary Fence Looking New

A well-maintained fence does more than define property lines. It enhances curb appeal, improves privacy, and protects your outdoor space from unwanted intrusions. In a city like Calgary, where changing seasons bring everything from heavy snow and freezing temperatures to intense summer sun, fences face constant exposure to harsh conditions. Without proper care, even a quality fence can lose its appearance and structural integrity over time.
Strategies for Building a Reliable Transportation Workforce

The transportation industry keeps economies moving. From food and medical supplies to retail products and industrial equipment, nearly every sector depends on efficient logistics. Yet one challenge continues to affect fleets of all sizes: building and maintaining a dependable workforce. Driver shortages, changing regulations, and increasing customer expectations have made talent acquisition and retention more important than ever. Companies that invest in workforce development are better positioned to maintain service quality, reduce turnover, and remain competitive in a demanding market.

The "Macs Don't Get Viruses" Myth Is Officially Dead in 2026

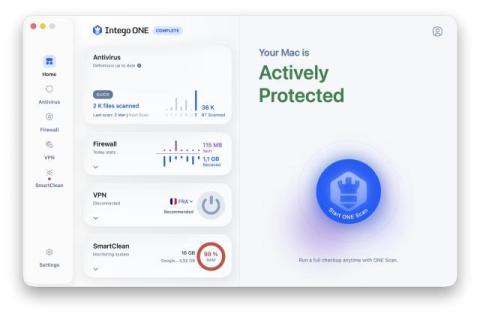
For many years, Apple users have believed that Mac computers are naturally protected from cyber threats. This perception was shaped by the relatively low number of attacks targeting macOS in the past. However, the cybersecurity environment in 2026 presents a very different reality. As Apple's global market share has expanded and Mac users have become increasingly valuable targets, cybercriminals have shifted their focus toward developing attacks specifically designed for macOS.

Why crypto companies still struggle to gain banking trust

The cryptocurrency industry has made significant progress in regulatory compliance over the past several years. New licensing frameworks and stricter anti-money laundering requirements have raised standards across the market. Even so, many legitimate crypto businesses continue to face difficulty when opening or maintaining banking relationships.

Why network vulnerability management is critical for businesses and how to automate it

Network vulnerability management is no longer a periodic security task. As networks expand across locations, vendors, and OSs, vulnerabilities can emerge quietly through configuration changes, outdated firmware, or delayed patching. Without consistent visibility and automation, teams often discover risks only after they affect availability, security, or compliance. Effective vulnerability management requires continuous awareness, structured assessment, and controlled remediation.

7 Best Practices for Privileged User Monitoring

With great power comes great responsibility — and in the cybersecurity world, immense risk. Your privileged users hold the keys to your organization’s digital kingdom. They have the elevated permissions to keep your infrastructure running, but this means a single compromised account or insider mistake can result in a catastrophic data breach. That’s where privileged user monitoring becomes non-negotiable.

NVD in the AI Era: The Case for Multi-Source Vulnerability Intelligence

For over twenty years, the global security community has operated under a single, comfortable assumption: that a centralized public source could help track, analyze, and enrich the world’s software vulnerabilities at the pace the industry needed. When the National Vulnerability Database (NVD) was established, the open source vulnerability lifecycle moved at a radically different pace.

Automation in Security: Fast Track to Compliance

Manual security operations don't just slow teams down. They make breaches more expensive. Organizations that implement advanced security automation cut breach response time by over 100 days and save an average of $3.05 million per incident, according to JumpCloud's 2024 analysis. That number reframes the conversation. Automation in security isn't a convenience feature for mature SOCs. It's an operating model.

Attestation in Cybersecurity: Types, Uses & Best Practices

Attestation is a security process that enables one system or entity to prove its state or characteristics to another. This typically involves generating verifiable evidence about the software, hardware, or configuration of a device or environment. The primary goal is to ensure that systems are operating as expected and have not been tampered with. Attestation is important for building trust in distributed environments, where direct oversight and control are not always possible.

AI Inference Risk: The Data Exposure Your DLP Can't See

Your DLP controls are correctly configured. Classification policies are in place. Sensitive data is labeled. And your AI tools are quietly building a picture of your organization that none of those controls can see. Most AI-related data exposure does not arrive as a file transfer event.