Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Brand Impersonation is moving into the App Store

Apple's 2025 App Store Transparency Report states that the company blocked over $2.2 billion in fraudulent transactions and removed roughly 59,000 apps for bait-and-switch tactics: publishing one thing to gain approval, then swapping in something else once the app goes live. The year before, fraud accounted for 38,315 of Apple's 82,509 total app removals, roughly 46%, making it the second-largest removal category that year. Google's numbers point in the same direction.

Online Gambling Fraud: How Fake Sites, Apps and Social Ads Divert Player Deposits

Online gambling fraud includes more than bonus abuse, payment fraud, account takeover and suspicious withdrawals on a genuine betting platform. Fake gambling sites, cloned apps and deceptive social ads can capture players before they reach that platform, diverting registrations, credentials and deposits into an attacker-controlled or unlicensed environment.

Social Engineering Campaign Uses Phony NDAs to Avoid Detection

Researchers at Gen Digital are tracking a sophisticated social engineering campaign that’s using phony NDA documents to trick employees into moving the conversation to WhatsApp and personal email accounts. The attackers targeted an employee at Gen itself, but the employee recognized that it was a scam and played along to see what the attackers would do. The threat actors first impersonated a real Gen executive based in Dublin, who introduced a second impersonated person who claimed to work at PwC.

Survey: Companies Cite Phishing as their Top AI-Enabled Fraud Concern

A recent survey from Experian found that 60% of companies report fraud losses that are “somewhat or significantly higher” than in previous years, with a majority of respondents citing AI-generated phishing attacks as their top AI-related fraud concern. “Businesses identify AI-generated phishing as the most common AI-enabled fraud risk at 53%,” the report says.

Your CFO Just Left You a Voice Note. It Wasn't Her.

A voice note from your CFO on WhatsApp. Her cadence, her urgency—and a reference to a confidential acquisition discussed in a real meeting last Tuesday. North Korea's Blue Noroff builds these backwards: compromise a junior employee's calendar or inbox first, then train a voice model on the stolen context. By the time anyone thinks to verify, the emergency transfer is already sitting in an offshore account.

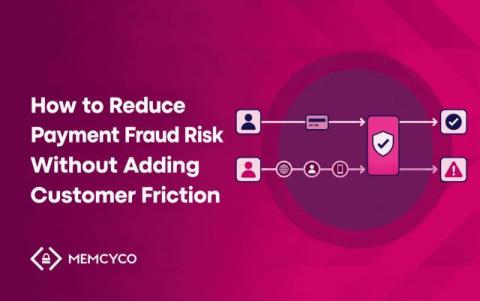
How to Reduce Payment Fraud Risk Without Adding Customer Friction

Reducing payment fraud risk requires giving existing fraud controls enough context to distinguish higher-risk interactions from routine activity, rather than applying more checks to every customer. That distinction matters. UK Finance reported that criminals stole almost £1.3 billion through authorized and unauthorized fraud in the UK during 2025. Authorized push payment fraud alone accounted for £576.4 million, up 19% year over year.

How AI Phone Calling Is Changing Voice Phishing Defense

Phone scams have been around for decades, but the last few years have brought a sharp shift in how convincing they've become. Voice phishing, often called vishing, used to rely on generic scripts and a scammer's ability to sound believable. Today, the same technology that powers helpful tools like AI phone calling is also being studied and used to fight back against these scams.

Twitter Brand Impersonation: How Security Teams Detect Fake Accounts and Phishing on X

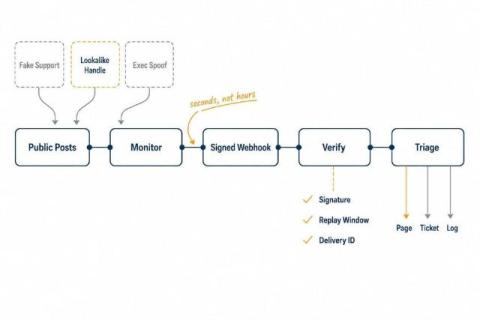
Most brand impersonation starts in public. A lookalike support handle appears, replies to real customers under your official account, and links to a credential-harvesting page. By the time it reaches a takedown vendor's weekly report, the damage window has been open for hours.

Why slow fraud investigations cost more than you think: The ROI case for AI-assisted investigation

Fraud doesn’t wait for your investigation queue. Every minute an alert sits unresolved gives fraudsters more time to move the money. Yet at most financial institutions, a single case still takes an analyst 10 to 30 minutes to investigate — pulling transaction history, checking device and behavioral data, weighing risk signals and documenting a decision. Multiply that by hundreds or thousands of alerts a day, and slow investigation isn’t just an inconvenience.