Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

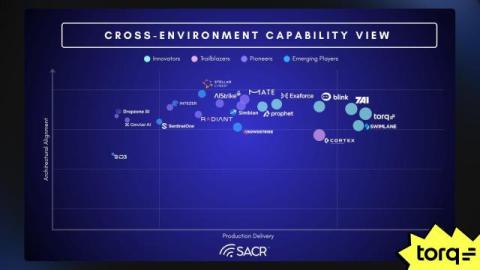
Torq Named a Leading Innovator in SACR 2026 AI SOC Market Report

Software Analyst Cyber Research (SACR) just published its 2026 AI SOC Market Report, offering an independent assessment of vendors competing in what has rapidly become the most consequential category in enterprise security. Torq features prominently, and the report’s framing is worth unpacking because it illuminates what makes the AI SOC category hard to evaluate and why Torq’s approach is consequential.
Featured Post

Solving the SOC Data Dilemma: Maximising Detection Without Maximising Cost

Today's Security Operations Centres (SOCs) operate under the pressure of data proliferation, high alert volumes, and tight budgets. Most SOC leaders face a data dilemma: they must choose which data to analyse and which to ignore. That choice directly determines threat detection capabilities and impacts the security posture of the business.

Torq SOC Brain: The AI SOC That Learns, Not Just Remembers

Back in June, I wrote a blog making the case that agentic triage alone isn’t an AI SOC. The way I see it, that’s like saying triage is the only responsibility of a SOC team. But as we know, the SOC’s responsibilities extend far beyond that, and these triage-only solutions don’t investigate threats, contain them, or close cases. That work is still left to the SOC team; the bottleneck is just shifting.

The Howler Episode 32 - Diana Holtsman, VP, Finance PMO

This month, we sit down with Diana Holtsman, Vice President of PMO, to learn more about her journey to Arctic Wolf, how her role within Finance influences company strategy and decision-making, and so much more! Diana is VP, Finance PMO at Arctic Wolf where she supports both the CFO and CEO — keeping the company's biggest priorities moving across strategic planning, operating cadence, board readiness, and cross-functional initiatives. In working across both the finance and executive offices, she has a rare vantage point on how the whole company fits together.

Understanding Context Windows in AI-Powered Security Operations

Your security operations team now relies on AI agents to detect threats, triage alerts, and accelerate incident investigation. These agents analyze signals across your environment to identify suspicious behavior that humans might miss, and they respond faster than any manual process could. But they operate under a fundamental constraint that most security teams overlook: context window limitations that directly impact investigation quality and threat visibility.

The 2026 AI SOC Roadmap: Where SOC Teams Are Headed and How to Get There

Every conversation our team has with security leaders begins the same way. Nobody is backing off on AI in the SOC. The direction of the lean is what’s shifting. Torq’s 2026 AI SOC Leadership Report surveyed more than 450 CISOs and SOC leaders. The data confirms what those conversations were already telling me. We’ve left the adoption phase. The market is now in the architecture phase and the implications for how teams plan, buy, and build are significant.

Elevating the SOC Experience: Smarter Automation, Richer Threat Intelligence, and AI-Native Investigation

Security operations teams face a constant balancing act: stopping sophisticated email threats, maintaining visibility across their attack surface and keeping administrative workflows running smoothly. When security tools operate in silos or rely on rigid, manual processes, friction builds up quickly. This friction consumes valuable time that analysts could spend on higher-priority initiatives. At KnowBe4, we believe enterprise security should work for you, without the enterprise-grade costs.

Cyber Threat Intelligence: How to Build a Practical Programme for Your SOC

As cyber dangers get more sophisticated and messy, company SOCs can't simply keep playing defense. An effective IT security strategy today includes hunting malicious agents down before they strike. Modern organizations need a thorough grasp of the tactics, techniques, and procedures used by industry-specific adversaries.

Resolve: One-Click Patching from Aurora Vulnerability Management

Vulnerability discovery is only half the story; remediation is where breach potential gets reduced. Resolve, part of Arctic Wolf's Aurora Vulnerability Management, brings one-click patch deployment across Windows, Mac, and Linux so security teams can move from "we found it" to "we fixed it" without the manual overhead. In this overview, see how Resolve turns vulnerability data into action: one-click patch orchestration, flexible scheduling, and clear visibility into remediation status — all inside the Aurora platform.

What Headless Actually Means for Security Operations

Co-founder and COO LimaCharlie founder Maxime Lamothe-Brassard joined Alex Hurtado on the Detection Dispatch podcast to talk about the shift happening across the industry: security capabilities moving out from behind the UI. When every platform function is reachable through an API or CLI, both humans and AI agents can do the work without logging into a console. The episode covers what headless means in practice, how to govern agents in production, and where automation actually pays off.

AI-Powered Cybersecurity at Machine Speed | Arctic Wolf

AI is accelerating cyberattacks, pushing security teams to their breaking point. Arctic Wolf helps organizations get ahead and stay there with the Aurora Superintelligence Platform, combining AI that is built in, not bolted on, with human validation and 24x7 security operations. See how Arctic Wolf helps protect more than 10,000 customers.

Building Trust in AI for Cybersecurity | Arctic Wolf

Cybersecurity has reached a turning point. As defenders embrace AI, the question is not simply whether it is powerful, but whether it can be trusted to deliver real value. The Arctic Wolf Aurora Superintelligence Platform brings together trusted AI, real-world data, and human expertise to help transform security operations with reliability, governance, and results.

How to Patch Vulnerabilities and Reduce Risk with Aurora Vulnerability Management and Resolve

Learn how to identify, prioritize, and remediate vulnerabilities using Aurora Vulnerability Management and the Resolve integration. This demo walks through filtering and targeting high-risk vulnerabilities, deploying patches across assets, and tracking patch jobs to reduce risk more efficiently.

20 Questions Every Security Leader Should Ask Before Buying an AI SOC

Most “AI SOC” demos out there can look great. The polished dashboard, the confident verdict, the slide that says “autonomous.” A demo is built to show the platform at its best, on clean data, in a controlled environment, answering a question the vendor already knew was coming. The differences only show up after you’ve signed, when the platform meets your real stack, alert volume, and compliance requirements.

How to Gain Flexibility and Maximize Security Improvements with Self-Service Security Reviews

In this demo, we will see how Arctic Wolf security posture reviews and the self-service capability deliver high quality recommendations and give customers the flexibility to maximize posture improvements at their own pace.