Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Aembit Extends IAM for Agentic AI to Microsoft Copilot Studio

Aembit on Tuesday announced support for Copilot Studio, extending its identity and access management capabilities to Microsoft's enterprise AI agent platform. The integration, unveiled at Identiverse 2026, gives security teams the tools to manage what Copilot Studio agents can access, under what conditions, and with a complete record of every decision. The company also released an interactive enterprise AI readiness checklist to help organizations assess their agent deployments before they go into production.
Teleport Debuts Delegated Agentic Identity and LLM Proxy in Beams Public Beta, for Containing Agents in Production Infrastructure

Two foundational identity concepts - controlling the scope of agent roles and constraining what they can access - now have a production implementation in Beams, Teleport's trusted, ephemeral agent runtime.

Agentic IAM: The Complete Guide to Identity Security for Autonomous AI Agents

If you’ve deployed your first AI agent, then you must have given it access to your CRMs, ticketing systems, and your cloud storage. This AI agent is programmed to run 24/7, make decisions, call external APIs, and trigger actions (without a human in the loop). Now, answer these questions: If you cannot answer these questions, then you have an agentic AI identity issue. Traditional Identity and Access Management (IAM) was built for service accounts with static API keys and users with usernames.

How to build AI agents your security team will approve

A security engineer spends three weeks building an AI agent that triages phishing reports. The demo lands well. Then it hits the security review queue, and the questions start: Which tools can it call? What happens if it misclassifies? Who approves an account lockout at 2 a.m.? Where are the logs? Three more weeks pass, and the agent is still sitting in staging. This is the pattern most teams run into. The agent works, but the governance story doesn't.

Why Agentic AI Is Finance's Biggest Security Blind Spot

An AI agent with access to a customer’s brokerage account can begin executing trades. Not because the customer asked. Because someone, somewhere upstream, slipped a hidden instruction into a tool the agent loaded at startup. The agent is doing exactly what it was told. Just not by the customer. This is not a hypothetical. It is the attack class that financial security teams have exactly zero legacy tooling to catch and it is arriving precisely as banks accelerate their agentic AI ambitions.

The Role of Agentic AI in Phishing Security Training

Phishing attacks are evolving faster than traditional training programs can keep up. Advances in AI — including generative tools — are making attacks more dynamic, personalized, and harder to detect. At the same time, agentic AI for phishing security training is reshaping how programs improve, enabling them to adapt to user behavior and shifting risk in real time.

CERT-In's 12-Hour Patch Mandate: Is Your Organisation Ready to Respond at AI Speed?

CERT-In just published a risk-based remediation framework that resets expectations for every organisation operating in India. The timelines are worth reading twice: Now consider one question: if a known exploited vulnerability appeared on your internet-facing application at 11pm tonight, what would your team do in the next 12 hours?

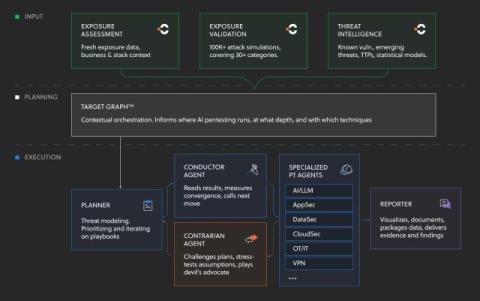
Continuous AI Pentesting: What We're Building, and What It's Already Finding

Over the past months, I’ve noticed a shift in customer conversations. Coverage, prioritization, emerging threats — those questions have given way to exposed MCP servers, unmanaged AI chatbots, and risks that don’t show up as CVEs. Mythos comes up in every other call. The calculus changed. AI now writes a quarter of production code, with twice as many vulnerabilities. The exploitation window collapsed from days to hours.

Cursor's Head of Security: Never trust the agent writing your code

"The hardest thing in security is always the chaos," according to Travis McPeak, Head of Security at Cursor. He shared this with Nancy Wang, CTO of 1Password, and Dev Tagare, Senior Director of Engineering at Google, on a recent episode of Zero-Shot Learning, the podcast about how AI gets built, secured, and deployed. "We're always going to have more that we have to be doing than we can actually do.".

Why AI Can't Verify Its Own Code and What That Means for Enterprise AppSec

AI models that generate code are also the best at exploiting it. Here’s why independent verification, not the model itself, is the only trustworthy answer. This month, the US government ordered Anthropic to suspend access to its most capable models, Mythos 5 and the newly released Fable 5, for all foreign nationals, citing national security. The trigger was a single reported jailbreak that let one of those models slip past its own guardrails on cybersecurity tasks.