Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

OpenAI's Sol, Terra, Luna Explained: Which One Should You Use?

-OpenAI has completely overhauled its model naming system with the release of GPT-5.6, introducing three distinct tiers: Sol, Terra, and Luna. In this video, we put OpenAI's new flagship model, GPT-5.6 Sol, to the ultimate test. Using the Codex extension in VS Code, we throw our classic "Build me a secure notes app or I get fired" prompt at Sol. Watch as we break down the pricing and reasoning differences of the new tiers, run a full security audit using Snyk, and see if Sol's $5/$30 price tag is truly production-ready or if a small local CSRF bug gets us "fired" first.
How to Securely Roll Out Enterprise AI in 90 Days #shorts #aisecurity

Planning an enterprise AI rollout in 90 days? Establishing a robust AI Gateway Architecture is the critical first step to ensuring data compliance, enforcement, and security. Letting application traffic run straight to LLMs exposes your organization to severe security and compliance liabilities.

Beyond the Model: Harnessing Frontier AI for Stronger Cyber Defense

Frontier AI is fundamentally changing the pace of cybersecurity. For defenders and adversaries alike, it compresses the time required to discover vulnerabilities, assess exploitability, and act. AI models can reason across entire codebases, identify complex vulnerability chains, and generate exploit paths at a speed and scale that was previously impossible. That's a breakthrough for defenders, but it's also a preview of how quickly adversaries will evolve.

Build vs. Buy AI App Development in 2026 (When Everybody Is an AI Expert)

AI expertise is cheap to claim these days. A short course, a couple of weekend projects, and a working prototype are usually enough for someone to call themselves a specialist. Getting an AI system to survive real production traffic is another matter entirely, and a lot of companies are learning that the hard way in 2026.

How I'd Plug the MiniMax M3 API Into a Coding Agent Without Rebuilding the Stack

Every time a promising new model shows up, I run through the same mental math before getting excited: how much of my existing agent setup survives the swap, and how much do I have to tear out and rebuild just to try it. Most of the time the answer is "more than I'd like," which is exactly why I ignore half the models that cross my feed. MiniMax M3 is one of the rare ones where the answer turned out to be "almost none of it," and it's worth walking through why, because the reasoning applies beyond just this one model.

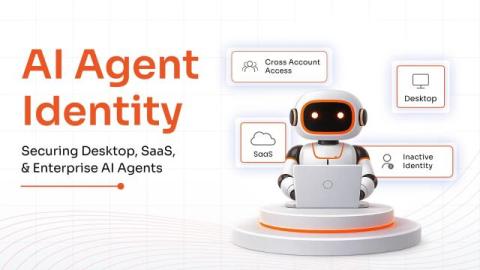
AI Agent Identity: Securing Desktop, SaaS, and Enterprise AI Agents

Your enterprise probably has a few thousand employees with managed identities. HR provisioned them, IT governs them, and your IAM platform watches them. Now count the AI agents running across your org. The Claude Code and codex instance that sit inside every dev's IDE. The Salesforce Einstein bot with access to every open deal. The Zapier AI that reads your CRM, writes to your Slack, and forwards summaries to email. You can't count, secure, or govern them with traditional IAM, can you?

Protecting PHI Beyond Names and ID Numbers

A few years ago, an Australian government health agency released what it believed was a fully de-identified dataset covering 10% of the national population. Names, addresses, and other obvious identifiers had been stripped out. Researchers showed individuals could be re-identified using nothing more than rare medical procedure codes and treatment dates cross-referenced with publicly available information. No names were needed.

Is the SaaS Market Is About to Collapse?

AI coding is disrupting the SaaS market. GRC tools, CRM products and enterprise dashboards that cost hundreds of thousands can now be built internally in weeks using Codex and other AI models. SaaS companies know this is happening, which is why they're locking customers into three to five year contracts. But there's a serious security risk nobody is talking about. If you're vibe coding internal tools and applications, you need continuous security testing to catch vulnerabilities before attackers do. The faster you develop, the faster you need to detect breaches.