Mailchimp
Not subscribed to OpsMatters Newsletter


Detectify is honored to start off the RSA 2023 Conference with the news that it has been recognized as the market leader in Attack Surface Management in Cyber Defense Magazine’s Global InfoSec Awards. This accolade demonstrates the effectiveness of Detectify’s approach to External Attack Surface Management (EASM), which is unique in the space because it tests environments with real payloads by using its crowdsourced community of ethical hackers.
We are thrilled to announce that GitGuardian has been honored with two prestigious awards from Cyber Defense Magazine (CDM) during the RSA Conference 2023!
With warm and sunny weather expected all week, a bunch of the Salt team is thrilled to be at RSA in San Francisco! We’ll get the chance to talk with security leaders about why API security has become a priority project, and we’ll get time to catch up with customers and each other. It’ll be a great week!
Cyber attacks have become inevitable. According to research from Rubrik Zero Labs, 99% of IT and Security leaders were made aware of a cyberattack against their organization in 2022 with an average of 52 cyberattacks in this category. On top of that, 96% of IT and Security leaders are concerned they will be unable to maintain business continuity if they experience a cyberattack this year.
Extended Validation (EV) Code Signing certificate is an advanced digital signature. It protects software developers’ and publishers’ codes, content, scripts, and other digital objects in their software and online applications from malicious attacks. EV Code Signing provides next-generation security and trusts to the customers by signing their software. The software publishers and developers must undergo stringent verification and inspection to obtain EV Code Signing Certificate.
For online gaming, player onboarding and Know Your Customer (KYC) processes are critical components of player engagement, retention, and compliance. Effective onboarding ensures that players can easily and quickly start playing games, while KYC helps protect operators from fraud, money laundering, and underage gambling. However, these processes can also create friction for players, leading to drop-offs and abandonment.
Security teams are faced with relentless cyberattacks, and they cannot engineer defenses fast enough. SOC teams face limited visibility, insufficient context, and the inability to identify the threats that matter. Analysts are even more burned out, switching from tool to tool, frantically trying to make sense of what they are seeing.
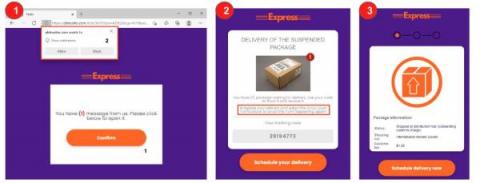
Netskope Threat Labs is tracking a phishing campaign that mimics a FedEx package delivery as bait to steal credit card data. This type of social engineering attack is commonly found in phishing pages, emails, and other scams, where a false sense of urgency is created to urge the victim into doing an action that eventually leads to personal data theft.
After COVID, enterprise IT security got turned on its head. As the world adjusted to working from home, and continues to, IT teams worked overtime to enable remote access for millions of employees. This transition has gone smoothly for most organizations, but many security gaps still remain years later. The SolarWinds data breach is a worrying example. It shows how vulnerable organizations are to malicious activity in our changing risk environment.