Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Latest posts

Tigera: Kubernetes Compliance: Implementing Network Security to achieve compliance with PCI, SOC2 and other frameworks

In today's regulatory landscape, securing Kubernetes environments and meeting compliance requirements is critical for many organizations. This hands-on workshop provides a comprehensive guide to achieving Kubernetes network security and compliance, with a focus on practical implementation.

Netskope: Unleash the Power of SASE: Expert Guidance from BMO, Airbus, and Orbia

Transitioning from legacy systems to modern SASE architectures can feel like upgrading from dial-up to high-speed internet-challenging yet essential. Now is the time to adopt a cloud-first approach that meets today's needs and prepares you for tomorrow. Learn how to ensure a smooth migration, optimize your security posture, and leverage SASE to drive business success in a cloud-first world. Join network leaders from BMO, Airbus, and Orbia as they share their insights.

Enhanced Threat Exposure Management with Seemplicity and OX Security

Managing vulnerabilities across multiple domains, and especially application security, is a challenging task for enterprise organizations. Security teams often find themselves grappling with fragmented tools and data, leading to inefficiencies and potential blind spots. Seemplicity’s recent integration with Ox Security addresses this issue directly, offering a unified approach to vulnerability management that bridges the gap between security, development, and operations teams.


How Cloudflare auto-mitigated world record 3.8 Tbps DDoS attack

Since early September, Cloudflare's DDoS protection systems have been combating a month-long campaign of hyper-volumetric L3/4 DDoS attacks. Cloudflare’s defenses mitigated over one hundred hyper-volumetric L3/4 DDoS attacks throughout the month, with many exceeding 2 billion packets per second (Bpps) and 3 terabits per second (Tbps). The largest attack peaked 3.8 Tbps — the largest ever disclosed publicly by any organization. Detection and mitigation was fully autonomous.

CrowdStrike Empowers DevSecOps Teams to Strengthen and Streamline Cloud Security

Support for cloud security posture management (CSPM) misconfigurations: Our enhanced CSPM tools vigilantly monitor cloud infrastructures for misconfigurations, compliance violation and security gaps, providing complete visibility into security posture early in the development cycle and saving SecOps teams time.

How to detect more bugs in AUTOSAR Applications and enable SiL testing by using a simulator

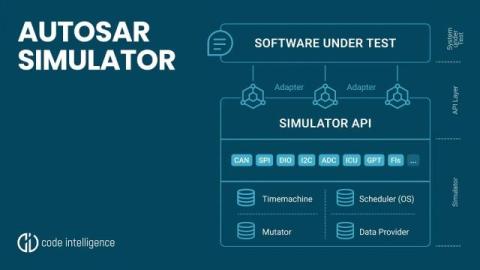
Testing Classic AUTOSAR applications has long been a significant challenge due to the reliance on hardware-in-the-loop (HiL) setups, which are costly, complex, and hard to scale. Code Intelligence’s new lightweight AUTOSAR simulator revolutionizes this process by enabling entire AUTOSAR applications to run on x86 Linux systems, thus facilitating software-in-the-loop (SiL) testing.

Complying with the EU's New AI Act: A Guide to Staying Ahead

Artificial intelligence (AI) is increasingly embedded in modern organisations—from standalone generative AI apps to AI copilots in popular SaaS platforms, and the integration of self-hosted or public large language models (LLMs) in private applications tailored to specific business needs. The recently introduced EU AI Act sets out to regulate AI development and usage, ensuring that AI systems are safe, ethical, and respect fundamental rights.