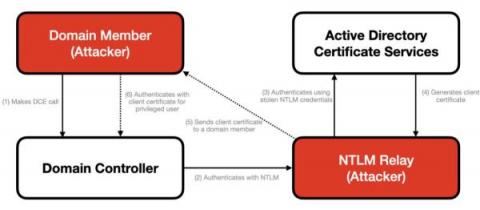
In July 2022, Microsoft disclosed a vulnerability in the Windows Server Service that allows an authenticated user to remotely access a local API call on a domain controller, which triggers an NTLM request. This results in a leak of credentials that allows an attacker to authenticate to Active Directory Certification Services (ADCS) and to generate a client certificate that enables remote code execution on a domain controller.
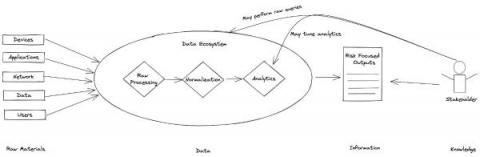
The saying “data is king” has been around for quite a while and we all know that the world operates and makes decisions on digital data 24x7x365. But, is data king in the field of cybersecurity? I believe that evidence - not data - is what is needed to speed defenders’ knowledge and response capabilities, so let's talk about both.
Evidence is the currency cyber defenders use to pay down security debt, balancing the value equation between adversaries and the enterprise. Defenders can use evidence proactively, identifying and protecting structural risks within our zone of control. Evidence can also be used reactively by supporting detection (re)engineering, response, and recovery activities, guiding us back to identifying and protecting structural risks.