Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Bitsight MCP and Agentic AI Workflows: A Practical 90-Day Guide

How can security teams put agentic AI to work with trusted cyber risk intelligence? Discover how Bitsight MCP and Bitsight AI Mode help teams investigate cyber exposure, prioritize vulnerabilities, assess third-party risk, and automate security workflows. In this 45-minute webinar, Bitsight experts Christina Chehade and Tadd Hopkins demonstrate practical ways to bring AI into cybersecurity operations, from natural-language investigations to repeatable agentic workflows. You'll also get a 30/60/90-day roadmap for moving from initial exploration to scalable automation.
The Best AI Vendor Risk Management Tools in 2026

Conventional vendor risk tooling asks whether a supplier will suffer a breach. For an AI provider that question is necessary and incomplete, because the larger exposure is what the provider does with your material while operating exactly as intended. ‍ Retention periods, training use, inference location and the model serving an endpoint are data governance questions rather than security ones. Most platforms in this market have no field for them, which is the first thing to check. ‍

Cyber Risk Quantification Vendor Evaluation Checklist

Buying a cyber risk quantification platform means asking a vendor to defend numbers that will end up in front of a board, an auditor, or a regulator. Most evaluation calls never press that hard. The questions below are the ones that separate platforms from each other, and they are written so that any vendor can answer them, including vendors who would beat Kovrr on several of the answers.

Web App Owners - You're on Notice. Your Low-Hanging Fruit Just Got Lower

Recent incident response investigations reveal how AI-assisted attackers are chaining web application vulnerabilities, credential theft, privilege escalation, and lateral movement into autonomous intrusion workflows. This article is part of an ongoing series from Sophos frontline security operations specialists, sharing the expertise they use to strengthen our industry-leading Managed Detection and Response (MDR) service and defend customers against evolving AI-era threats.

Proof-of-concept exploit released for PHP vulnerabilities (CVE-2026-109618, CVE-2026-109619)

In response to requests, this update consolidates the Sophos countermeasures that relate the PHP2Shelll vulnerabilities. SophosLabs has developed the following countermeasures to specifically detect activity associated with this threat. The next table lists additional pre-existing Sophos countermeasures that will likely address post-exploitation activity associated with these vulnerabilities.

Why AI Needs a Data Control Plane (Masking and Gateways Aren't Enough)

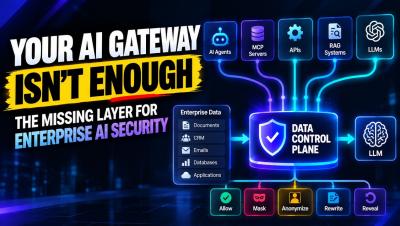
Your AI gateway and identity platform don’t decide whether a task can use a piece of enterprise data. In agentic AI, one request can trigger multiple agents, MCP servers, APIs, RAG systems, and LLMs, and each one is a separate security decision. This video explains why enterprise AI needs a runtime data control plane. It covers why identity alone can’t make the call, why masking PII isn’t enough when business context is sensitive, and how Protecto applies allow, mask, anonymize, rewrite, or selective reveal decisions across the AI workflow. It ends with a Fortune 100 multi-agent example.

Acronis Cyber Protect Cloud is now Acronis Cyber Platform

Until October 14, 2026, services providers have known Cyber Platform as Acronis Cyber Protect Cloud, whereas corporate customers have known Cyber Platform as Acronis Cyber Protect. To simplify partner, customer and user experience, Acronis offerings for both service providers and end-customers are renamed to Acronis Cyber Platform.

CISO Risk Intel Brief: Trusted Ingress, Edge Zero-Days, and AI-Generated Code Define Residual Risk

This briefing covers material developments for the seven-day period of 14–21 October 2026 and the thirty-day period of 21 September–21 October 2026. It is written for board risk committees, peer CISOs, and security leadership. The focus is residual risk, control effectiveness, and business enablement across application security, software supply chain, cloud and infrastructure, identity, third-party exposure, and AI-assisted development.

Smaller Models for Better Document Understanding

At Cyberhaven, we replaced our previous LLM-based approach to document understanding with a small model that makes 83% fewer decision errors at less than 1% of the inference cost. We achieved this by breaking complex tasks into simpler decisions, using uncertainty as a training signal, and heavily optimizing our inference stack. The model produces calibrated decision probabilities while preserving multimodal understanding and generative capabilities.

LiteLLM compromised again: infostealer and RAT found in version 1.107.0

On October 21, 2026, version 1.107.0 of LiteLLM (a popular open source proxy that lets developers route requests across dozens of LLM providers) was found to be compromised by an attacker who injected malicious code into its published Python wheels on PyPI. The official Docker image for the same version is also compromised.