Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How Internal Audit Can Raise the Bar on Fraud Risk Management

In a recent webinar, speakers from Kroll and Institute of Internal Auditors (IIA) Hong Kong discussed the findings from a global IIA/Kroll fraud risk survey. The findings of the research include perceptions of the effectiveness of a fraud risk management program in organizations, including prevention, detection and response; the tools used in the fight against fraud; instances of fraud versus perception; the tone from the top; and resourcing for successful fraud risk management in an organization.
Protecting Against the Unpatched Kubernetes Vulnerability (CVE-2020-8554)

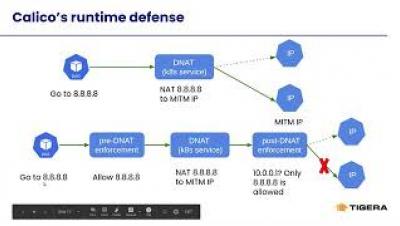
CVE-2020-8554 is a vulnerability that allows Kubernetes Services to intercept cluster traffic to any IP address. Users who can manage services can exploit the vulnerability to carry out man-in-the-middle (MITM) attacks against pods and nodes in the cluster. All Kubernetes versions including the latest release (v1.20) are vulnerable to this attack. If your cluster is multi-tenant, or allows unprivileged users to create and update services, you are impacted.