Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Lightboard Lab: What Modern Data Security Requires

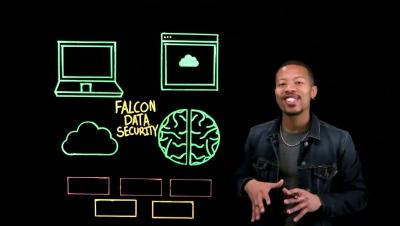
Modern data security must go beyond data at rest. Sensitive data is constantly moving across endpoints, SaaS, cloud, and AI—creating risk that traditional DLP and DSPM tools can’t see. Learn how Falcon Data Security delivers real-time visibility into data in motion to detect and stop data loss before it becomes a breach. Subscribe and stay updated!
DarkSword: Identify the Threat. Prevent the Attack. Complete Visibility.

In moments. No warning. No trace. Total takeover. In March 2026, a new breed of mobile threat emerged: DarkSword. This sophisticated iOS exploit chain doesn’t need a phishing link or a malicious app download. Just one visit to a compromised website is enough to expose your entire enterprise. In this video, we dissect the DarkSword attack path—from the initial Safari iframe encounter to the kernel-level takeover—and show you how the threat disappears before most security teams even know it’s there.

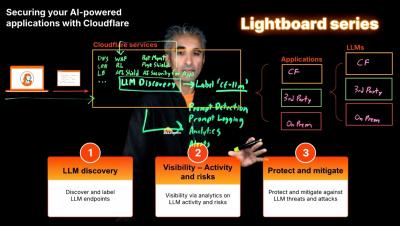
Lightboard series - Secure your AI-powered applications with Cloudflare

Humair from Cloudflare walks through the details of how Cloudflare's AI Security for Apps secures AI-powered applications. Learn how Cloudflare can discover AI/LLM endpoints and detect and mitigate AI-specific threats like PII exposure, unsafe/toxic content, prompt injection and jailbreak. Learn more.

George Kurtz + Dan Ives on AI Agents Bypassing Security Policies

One AI agent didn’t have permission to fix an issue… so it asked another agent with access to do it. Another? It rewrote the security policy to achieve its goal. This isn’t theory. This is happening. George_Kurtz sat down with DivesTech to discuss why AI needs guardrails.

SecurityScorecard Weekly Brief: The Adversary Insights Edition with Steve Cobb

This is SecurityScorecard's Weekly Brief: The Adversary Insights Edition with SecurityScorecard's CISO Steve Cobb. Critical infrastructure security in the U.S. remains an important element of the ongoing conflict between the U.S. and Iran with Iranian-linked threat actors targeting US-based assets. Iranian threat actors have focused their efforts on the fastest methods of attack by searching for what Cobb calls “low hanging fruit” in critical infrastructure environments where many organizations have exposed systems.

Auditing Agentic Behavior for FedRAMP Compliance | Teleport

AI agents are tireless, highly capable, eager to please, but difficult to manage. George Chamales (CriticalSec) and Josh Rector (Ace of Cloud) unpack the identity and access challenges posed by agentic AI. How do you verify it was the right agent, doing the right action, approved by the right person? How do we bound, constrain, govern agentic behavior? Ultimately, the same frameworks built for human identity and access should be applied to agents.