Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The Cyber Outage That Ends Before the Recovery Does

An interruption model measures the time from failure to restoration. Systems down, systems back, multiply by revenue per hour. ‍ In an airline the outage ends well before the recovery does, and the ratio between the two is large enough to make a model keyed to restoration wrong rather than imprecise. One carrier restored connectivity in under an hour and the resulting displacement ran into the following morning. ‍
AI Agents Were Never Outside the Definition

The word agent appears nowhere in the AI Act. Some read that absence as a scope question still to be settled, and treat agentic deployments as sitting outside a regime written before they existed. ‍ On its own FAQ the Commission has answered it directly. Agents are not a separate category and the existing definitions already reach them, so nothing needs amending for the rules to apply.

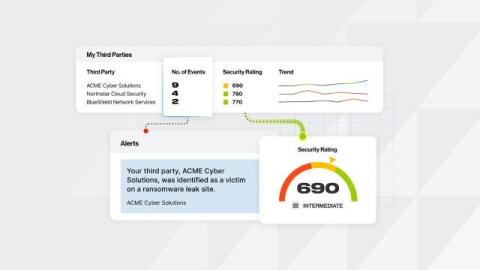
Know What's Actually Happening to Your Suppliers, Not Just When Their Names Show Up in Threat Data

A vendor can pass every questionnaire you send it and still be the reason you end up in a breach report. That's the gap most third-party risk programs live in today. According to the 2026 Verizon Data Breach Investigations Report, 48% of breaches now involve a third party, up from 30% the year before and 15% the year before that. But most organizations still manage that risk with periodic assessments and separate threat feeds. Those methods can tell you whether a supplier passed a review last quarter.

Beyond Alerts: What the 2026 Gartner Market Guide Says About the Future of MDR

Managed Detection and Response has long helped organizations extend their security operations capabilities, but buyer expectations are changing. Detecting suspicious activity and notifying internal teams is no longer enough. Organizations increasingly expect MDR providers to help investigate incidents, contain threats, identify exposures, and deliver measurable improvements to their security posture.

Introducing Salt Claude Connect: Continuous MCP Server Visibility for Claude Enterprise

As AI adoption accelerates inside enterprises, security and IT teams are increasingly asking a foundational question: what exactly is connected to our AI, and what can it access? For organizations running Claude Enterprise, Salt now has a direct answer. Salt Claude Connect links Salt to Claude’s Compliance API and provides continuous, read-only visibility into the MCP (Model Context Protocol) servers connected to your Claude Enterprise organization.

Detectify Cyber Hygiene Index Report reveals that most critical vulnerabilities sit unfixed for months

The Detectify Cyber Hygiene Index Report H2 2026 measures something most reports ignore: not what happened after an attack, but what’s exposed right now, before one occurs. We analyzed anonymized data from a sample of +1290 organizations across the US, UK, and Nordics to understand how effectively they’re finding, monitoring, and closing vulnerabilities across their external attack surfaces.

FBI Winter SHIELD's Cybersecurity Controls Are Worth a Second Look

AI adoption is making everyone faster, including the attackers we as cybersecurity practitioners are competing with. While the attackers are getting faster thanks to AI, it’s not changing why most preventable breaches happen. That part is remaining consistent, for better or worse.

Mobile App Security: Reverse-Engineering APKs and IPAs to Uncover Hidden Attack Vectors

Buried in OpenAI’s evaluations of its GPT-6 Astra model sits a finding that mobile teams should sit with for a minute. The model reverse-engineered compiled software well enough to escape a browser sandbox and chain privilege-escalation flaws on a hardened operating system, according to the company’s published evaluations. Reading compiled binaries used to be specialist work priced in weeks, and now it’s something machines do quickly and well.

Beyond the Scanner: How Verified PoC exploits Prove True Business Risk

On September 1, OpenAI announced that its new model, GPT-6 Astra, had become the first to cross the “Critical” cybersecurity threshold in the company’s Preparedness Framework. Most coverage focused on the safety implications, and fairly so, but buried in the announcement sits a benchmark result that should change how every security leader reads their next vulnerability report.