Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

What is MTTD and MTTR?

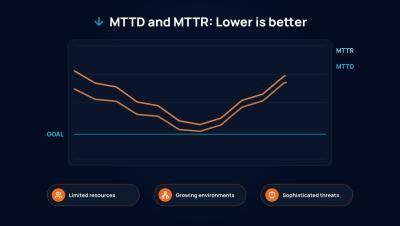
Meantime to detect (MTTD) and meantime to respond (MTTR) are two of the most important metrics for measuring a cybersecurity program. MTTD tracks how fast teams identify a threat. MTTR tracks how fast they contain and remediate it. The lower both numbers are, the less time attackers have to cause damage. Learn how to improve them with a clear incident response plan, defined roles, and around-the-clock security operations from Arctic Wolf.
What is Vulnerability Management?

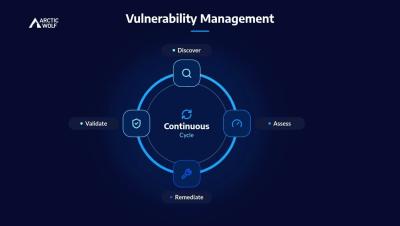
Every organization has vulnerabilities. The key is knowing which ones matter most and fixing them before attackers can use them. Vulnerability management is the ongoing process of discovering, assessing, remediating, and validating weaknesses across your environment. It is not a one-time project. It is a continuous cycle that reduces risk over time. Learn how risk-based vulnerability management helps security teams focus on the flaws most likely to affect the business. Arctic Wolf can help you prioritize and act before vulnerabilities become incidents.

What is a spoofing attack

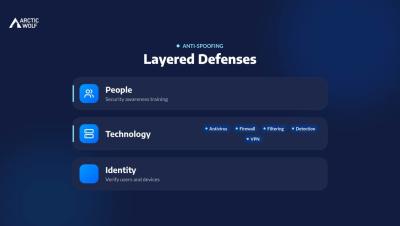
Spoofing attacks exploit trust. Attackers pose as people, organizations, devices, and websites to steal sensitive information or install malware. Learn how caller ID, email, IP, and website spoofing work. Then see how artificial intelligence (AI) deepfakes make impersonation harder to detect, and how employee training and layered security controls help stop these attacks. Want to learn more? Visit arcticwolf.com and explore our Cybersecurity Glossary to stay informed about evolving threats.

Why SecOps Is Essential for Modern Cybersecurity Operations

Security teams rarely lose to an attacker's brilliance. They lose to delay: an alert that sat in a queue, a patch that waited on a change window, a handoff between teams that nobody owned. As environments spread across cloud services, remote users, and connected devices, those delays get longer, and the cost of each one grows. Security operations, usually shortened to SecOps, exists to close those gaps. This article explains what SecOps is, why modern operations depend on it, and how to put it to work.

Arctic Wolf President and CEO Nick Schneider | @CRNvideo XChange Best of Breed Conference

How can organizations deploy AI responsibly without sacrificing trust, control, or accountability? At @CRNvideo's 2026 XChange Best of Breed Conference, Arctic Wolf President & CEO Nick Schneider joined CRN editors for a conversation on the role of AI in cybersecurity and what separates effective AI adoption from risky experimentation.

How does Aurora Adaptive Threat Protection stop advanced cyber threats?

Aurora Adaptive Threat Protection in Action: Stopping Ransomware Before the Damage Is Done What happens when a user clicks a malicious file that bypasses traditional defenses? In this demo, you'll see how Arctic Wolf Aurora Adaptive Threat Protection uses AI-powered, intent-based detection to identify and disrupt ransomware activity in real time, stopping attacks before encryption can spread across the environment.

Build vs. Buy AI SOC: A Decision Framework for CISOs

A Fortune 500 CISO recently told me, “If you are not implementing some form of autonomous threat detection and response, then even your best defenders will fall behind.” Attackers have weaponized AI and automation, driving up alert volume and threat sophistication. The use of agentic AI for defense is an absolute necessity to level the playing field. Security leaders now face a foundational decision: Build a homegrown AI SOC platform or buy a commercial one?

AI in the SOC: Where security teams stand

With 96% of security teams now using AI, the question is no longer whether AI delivers real value to the SOC, but one of efficiency and reliability. The recent AI Adoption in the SOC report, conducted by Dimensional Research and sponsored by Elastic, surveyed more than 400 cybersecurity professionals responsible for security operations at companies with more than 500 employees.

The Howler Episode 36 - Sam McLane, Chief Technical Services Officer

This month, we sit down with Sam McLane, Chief Technology Services Officer and one of Arctic Wolf's original team members, as he reflects on the company's journey from six employees to more than 3,500 worldwide. Sam shares lessons learned from nearly 15 years of building Arctic Wolf, why relationships have been at the heart of his career success, how he thinks about leadership, innovation, and staying ahead in the ever-changing cybersecurity landscape, and so much more!

2026 Security Operations Summit - Building Cyber Resilience Together

Two days. Hundreds of security leaders. Countless conversations about what's next in AI and cybersecurity. Thank you to everyone who joined us for the 2026 Security Operations Summit. From discussions on AI-driven security operations and cyber resilience to insights from industry leaders, the event was packed with ideas, innovation, and real-world expertise. We're especially grateful to our customers, partners, speakers, Cyber Resilience Leadership Award winners, and sponsors for making this year's event such a success.