Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Tooling Overview for API Testing (SAST, DAST, IAST, Fuzzing)

Application Programming Interface (APIs), allow services to communicate with each other. Naturally, applications that are interconnected through many APIs, require thorough security testing, as each connection could potentially include software vulnerabilities. Since there are different methods to test these junctions, I want to briefly discuss the benefits and weaknesses of the most commonly used API testing methods in this article.
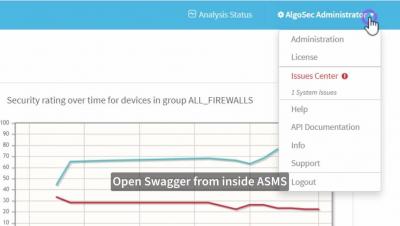
AlgoSec API Swagger

On premise and in the cloud, AlgoSec simplifies and automates network security policy management to make your enterprise more agile, more secure and more compliant – all the time. The AlgoSec platform provides a set of Swagger API documentation, available right from the platform itself. Swagger enables you to execute API request calls and access lists of requested parameters.

Review API Scanning Results

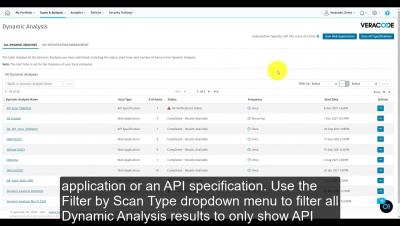
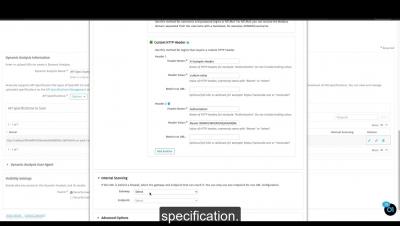
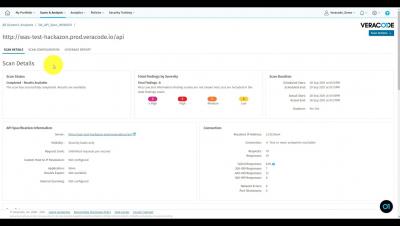
In this video, you will learn how to review Dynamic Analysis scan results for an API specification. After creating and submitting a Dynamic Analysis API specification scan, you can return to the list of Dynamic Analyses at any time to check for status updates and to view results. Please note, you must have the Creator, Reviewer, or Security Lead role to be able to view the results of a Dynamic Analysis, unless the results are linked to a Veracode application profile for which you have permission to view.

Review API Scanning Prescan Results

In this video, you will learn how to review Dynamic Analysis prescan scan results for an API specification. After creating and submitting a Dynamic Analysis API specification scan, you can return to the list of Dynamic Analyses at any time to check for status updates and to view results. Please note, you must have the Creator, Reviewer, or Security Lead role to be able to view the results of a Dynamic Analysis, unless the results are linked to a Veracode application profile for which you have permission to view.

The Good, the Bad, and The Ugly: Understanding the API Security Top 10 List

The Open Web Application Security Project (OWASP) is a nonprofit organization with the purpose to help secure software. They provide data that can give engineering and security teams a better idea of where the most common risks may lie. The 2021 OWASP Top 10, released in November 2021, lists the most critical web application security risks. But OWASP also maintains the API Security Top 10 project which was last updated in 2019. Each category is ranked based on the frequency and severity of the defect.

Continuous REST API Testing With CI Fuzz

CI Fuzz is a platform for automated security testing that aims to enable developers to ship secure software fast. The platform empowers development teams to automatically deploy continuous REST API security tests with each pull request. Since it enables the instrumentation of entire web service environments, CI Fuzz can create test inputs that are guided by code coverage. This enables it to uncover complex vulnerabilities and edge cases that other tools often overlook.

Why authorization and authentication are important to API security - and why they're not enough

The number of machine identities for which organizations are responsible has “exploded” in recent years, according to Security Boulevard. These machine identities include devices and workloads. But they also include application programming interfaces (APIs). Organizations use APIs to connect the data and functionality of their applications to those managed by third-party developers, business partners, and other entities, per IBM.

Phishing operators abuse bank APIs to improve phishing TTPs

True Login phishing kits are continuously being developed by threat actors to improve their TTPs in luring victims. By using true login kits, the phishing operators have a higher chance of making potential victims believe they are logging into the real website. True login kit developers are abusing publicly available APIs of the banking company to be able to query login information to be shown to potential victims, in turn luring the victim even further into the operations.

Create an API Specification Scan

Traditionally Veracode Dynamic Analysis has targeted applications with a Web user interface. But increasingly, web applications are composed of many small microservices, many of which have Representational State Transfer (REST) interfaces with which the UI layer communicates. With API scanning, you can now scan the APIs of your microservices earlier in the software development process, before they are integrated into a web application.

How and why we built Masked Email with JMAP - an open API standard

Our core values as a company center around our users’ privacy, security, and satisfaction. While developing Masked Email – our integration with Fastmail that lets users create new, unique email addresses without ever leaving the sign-up page – we needed a technology that brought all three values together.