Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Latest posts

Scaling your security team without hiring

The cybersecurity industry’s current struggle — to close a significant gap between the numbers of job openings and qualified candidates — began years before the coronavirus pandemic sparked the Great Resignation. Today, (ISC)² reports a global cybersecurity workforce gap of 2.7 million people. The pandemic did compel enterprises to accelerate their migration of applications to the cloud, increasing the challenge for already-overwhelmed security teams.

Supply Chain Security Intro Workshop

More and more attacks are aimed at the entire supply chain, which means that we developers are increasingly targeted by the attackers. Attacks like the SolarWinds hack show us that making sure you don’t use vulnerable dependencies isn’t enough. The attackers have their sights set on the entire development process with its components. In this workshop, we will look at the first steps and try them out in practice which will enable you to integrate the topic of security into your everyday life as a developer.

5 Steps to Stop the Latest OpenSSL Vulnerabilities: CVE-2022-3602, CVE-2022-3786

The OpenSSL Project team announced two HIGH severity vulnerabilities (CVE-2022-3602, CVE-2022-3786) on October 25, which affect all OpenSSL v3 versions up to 3.0.6. These vulnerabilities are remediated in version 3.0.7 which was released November 1. OpenSSL 1.X versions are unaffected by the vulnerabilities.

Can Privacy Exist in the Metaverse?

Although still in its early stages, the Metaverse is well on its way to becoming a full-blown reality. This monumental achievement was only made possible by the pandemic speeding up the implementation of VR and at-home digital services and by the subsequent penetration of these services among all demographic groups, especially younger people. But as the world steams forward into the great digital unknown, very few people are asking the fundamental question: is the Metaverse what humanity needs right now?

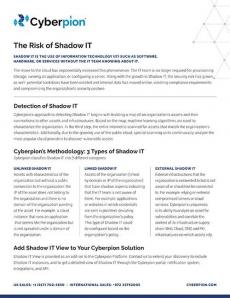
The Risk of Shadow IT

The move to the cloud has exponentially increased this phenomenon: The IT team is no longer required for provisioning storage, running an application, or configuring a server. Along with the growth in Shadow IT, the security risk has grown as well. Potential backdoors have been created and internal data has moved online, violating compliance requirements and compromising the organization's security posture.

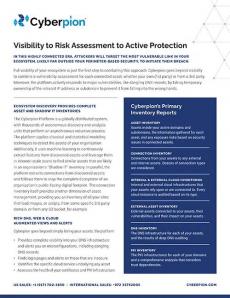
Visibility to Risk Assessment to Active Protection

Full external attack surface visibility is just the first step to safeguarding your organization. Cyberpion goes beyond visibility to combine an attack surface vulnerability assessment for each connected asset, whether your own (first party) or from a third party. Moreover, the platform actively responds to major vulnerabilities, like dangling DNS records, by taking temporary ownership of the relevant IP address or subdomain to prevent it from falling into the wrong hands.

Tigera: AWS Dev Days: Hands-on workshop: Implementing container security on EKS

Attend this in-depth, hands-on, EKS-focused security workshop with AWS Dev Days and Calico experts to learn how to prevent, detect, and stop breaches in applications running on EKS. The 90-minute interactive lab comes with your own provisioned Calico Cloud environment and a sample application. You will leave this workshop with hands-on experience on how to: We have limited the number of participants for this workshop to ensure that each participant can receive adequate attention.

WatchGuard: The Critical Factors to Look for in a Cybersecurity Vendor

Are you assessing which cybersecurity vendor to use for your business, or even consolidating to just one? There are some key characteristics and business strategies you'll want to consider. We've turned to global business leaders to share their experience vetting cybersecurity vendors and even trends in the security industry that influenced their choice. WatchGuard's Chief Information Officer Wayson Vannatta will host our four panelists.