Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Latest posts

Tigera: Microsoft Azure: Kubernetes and container networking for single and multi-cluster environment

In this AKS networking workshop, you will work with Microsoft Azure and Calico experts to learn how to design, configure, deploy, and secure your Kubernetes network for single and multi-cluster environment across Standard Linux, eBPF, and Windows dataplanes. This 90-minute hands-on lab comes with your own provisioned Calico Cloud and a sample app environment.

Vanta: The Future of GRC

As the need for security surges, the bar for proving and maintaining trust gets even higher. But many companies are left to wonder: are their GRC strategies and solutions setting them up for the future-or holding them back? This time on Vanta Delivers, Jeremy Epling, Vanta's CPO, will demonstrate exciting new product updates designed to help forward-thinking security teams scale their GRC programs.

KnowBe4: Ridiculously Easy Security Awareness Training and Phishing

Old-school awareness training does not hack it anymore. Your email filters have an average 7-10% failure rate; you need a strong human firewall as your last line of defense. Join us for a live demonstration of how KnowBe4 introduces a new-school approach to Security Awareness Training and Simulated Phishing. Get a look at THREE NEW FEATURES and see how easy it is to train and phish your users. Find out how nearly 70,000 organizations have mobilized their end-users as their human firewall.

Data classification: The fundamental requirement of successful DLP programs

The way we store data has undergone a dramatic shift. From good ol’ floppy disks to today’s cloud storage solutions, advancements in storage have slashed costs and allowed organizations to hold exponentially more data. And we are all taking advantage of this. In fact, data is proliferating at a staggering 25% annually. This presents a double-edged sword. On the one hand, this vast data lake holds immense potential for valuable insights.

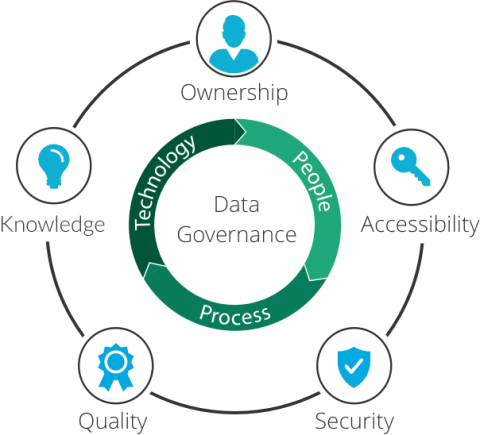
Top 10 data governance tools for 2024

While artificial intelligence and big data steal the spotlight, a less glamorous but equally crucial discipline is quietly shaping the future of business: data governance. With European regulators imposing fines of up to 17.29 million pounds for data mismanagement, it’s clear that data governance is not just a compliance checkbox. It’s a strategic investment that can empower your organization with a tangible return on investment.

The Power of Tripwire Enterprise SCM Policies

There are many good business, security, and compliance reasons for leveraging the extensive rule and policy engines of Fortra’s Tripwire Enterprise (TE) to implement Security Configuration Management (SCM) capabilities, which have been documented very well in other blogs. In contrast, this article deals more with “how can we fully leverage this capability” technically instead of “why” we use them.

Navigating Change: Three Levels to Filter Out the Noise in Tech Environments

Change is relentless. Technology evolves at breakneck speed, and security practitioners face a constant barrage of updates, system tweaks, and new tools. This relentless stream of modifications can create a clutter of information, making it challenging to pinpoint what is truly important. Effectively filtering through this noise through effective change management is critical for maintaining operational efficiency and security.

Using Honey Tokens for Threat Detection with Netwrix Threat Manager

Today, cyberattacks are no longer a matter of if, but when. Spotting malicious actors before they can do damage requires a proactive approach. One effective strategy is to use honey tokens. This article explains what honey tokens are and how Netwrix Threat Manager enables organizations to easily create and use them to gain the threat intelligence they need to shut down attacks and improve their security posture.

Identifying Common Open Port Vulnerabilities in Your Network

When intruders want to break into an establishment, they look for an opening. An open port is one of the openings that a hacker or threat actor looks for to access a digital network. That open port may be on a firewall, a server, or any network-connected computing device. Just as a single unlocked door can jeopardize your privacy and grant access to a physical building, a single open port can provide a point for hackers to breach your systems, exposing you to their malicious intents.