Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

When One AI Model Fails Many Companies at Once

Cyber insurance works because losses across a book are mostly independent. One insured suffering ransomware tells you little about the next, so a portfolio of many policies is more predictable than any single one. ‍ Shared AI dependencies break that assumption in a specific way. Where a large share of a book depends on the same foundation model or the same inference infrastructure, a single failure produces simultaneous claims across insureds with no commercial relationship to each other.
When scanners miss the attack: how Cloudflare Client-Side Security protects storefronts

A modern storefront can look perfectly healthy while malicious JavaScript works underneath: siphoning affiliate revenue, hijacking searches and clicks, tampering with analytics, or asking a remote server what to execute next. Pages load, products appear, and checkout works — yet the browser may be quietly doing something the site owner never authorized. That is the blind spot our Client-Side Security machine learning (ML) model is built to expose.

Top 7 API Security Tools for Banks and Fintechs in 2026

Every digital banking transaction today, whether it’s a fund transfer, a loan approval, or a balance check through a fintech app, runs through an API. API security for banking means protecting these connections from attacks that go far beyond simple hacking attempts: fraud rings probing for account access, bots automating fake transfers, and partners quietly overstepping the access they were given.

From Encrypted Mobile Traffic to Payment Manipulation

How KomodoSec’s AigentX Penetration Tester reverse engineered client-side encryption, turned the bypass into reusable Burp tooling, and used that access to validate a real business-logic flaw in a production mobile application. Client-side secrecy failed. Server-side trust became the real vulnerability. THE CHALLENGE A mobile app with TLS, certificate pinning, and a second encryption layer.

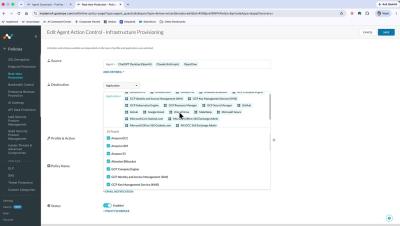
Demo - Agent Action Control

Netskope Skylight Agent Action Control is an inline security capability within the Netskope Skylight AI Security suite designed to evaluate, govern, and enforce real-time controls over the actions performed by autonomous AI agents. Rather than simply blocking or allowing an entire AI application or coding assistant, it intercepts attempted agent operations—such as code pushes, database modifications, or API calls—before they execute.

CrowdStrike Accelerates Real-Time Data Classification with On-Device AI

Modern data security depends on understanding sensitive data as it is created, accessed, and moved in real time directly on the endpoint. In addition to identifying predefined patterns such as credit card numbers or Social Security numbers, organizations must protect unstructured information including documents, chat logs, support tickets, AI prompts, medical records, and free-text fields.

AI anxiety is showing up on the org chart

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

The cache miss that made our agent faster

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Alert: AI is Accelerating Targeted Social Engineering Attacks

AI tools are drastically improving the speed of the reconnaissance stage of targeted social engineering attacks, according to researchers at ESET. Attackers can use these tools to trawl the internet for publicly available information about potential victims, and incorporate this information into personalized spear phishing attacks.