Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How AI Is Changing Portfolio Analysis and Financial Decision-Making

Want to make smarter money decisions without spending hours buried in spreadsheets? Wealth management has always been about number crunching. For decades, that crunching was done by humans armed with calculators, whiteboards and caffeine. Fast forward to today, AI can help you.
Sponsored Post

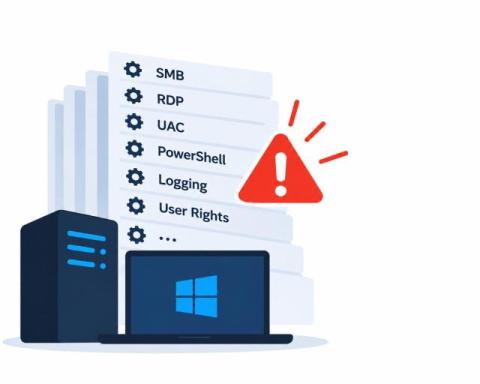
Windows Hardening & Continuous Compliance: Keeping 200+ Security Settings Secure 24/7

Every Operating System – not even counting the software installed on top of it – has a myriad of configuration settings that affect security. Windows Server alone has 4000+ configurable options, out of which 200+ are important for security & compliance efforts. They include: These settings are at the very core of all of your security & compliance efforts – and they are surprisingly often ignored.

Your CVE is reachable. But is it exploitable?

Any SCA tool worth its salt has reachability analysis these days. When a dependency has a known vulnerability, these tools can tell you whether your code calls the affected function. This is pretty much non-negotiable because it helps teams focus their security efforts instead of sifting through noise. Every other step in prioritizing dependency CVEs builds on it. But just because the vulnerable function is reachable doesn’t mean it’s exploitable.

MCP Database Security: Seven Boundaries Every AI Agent Needs

Connecting an AI agent to a production database can turn a slow investigation into a short conversation. The agent can inspect a schema, generate a query, and help explain a failed migration or an unexpected metric. The same connection can also expose sensitive records or modify production data if the access path is treated as a single trusted pipe.

AI guardrails aren't security controls

AI guardrails are sold as a solution to keep models behaving as intended - but it can be hard to figure out what you’re getting. The problem starts with the word itself. "Guardrails" means different things depending on who's selling them. Some vendors use it for simple prompt filtering, others bundle in entirely different controls and call it "guardrails" because the word sounds reassuring. Without a shared definition, buyers can't easily tell what they're actually getting.

Phishing Is Now A Criminal Impersonation Industry. Here Is How To Fight Back

For years, we described phishing as an email problem: an attacker writes a convincing message, sends it to thousands of people and waits for someone to click. That model is now outdated. Microsoft’s disruption of YAM Store, CoGUI and Iron Man exposed something much larger: a cloud-based impersonation industry.

Rubrik MSP Unscripted Episode 7 - Featuring Rajat Shah

In this episode of MSP Unscripted, Nawaz Ali sits down with Rajat Shah, Product Manager at Rubrik, to talk about the launch of multi-tenancy and what it means for managed service providers. Nawaz and Rajat discuss how shared infrastructure can help MSPs improve service economics while maintaining strong tenant isolation, expand opportunities across SMB and mid-market customers, and make services such as Backup as a Service, Disaster Recovery as a Service, isolated recovery environments, and advanced cyber recovery capabilities more scalable.

Anthropic's Free OSS Scanner: What It Means For Your Team

On October 8, 2026, Anthropic announced OSS Scanner, a free, opt-in vulnerability scanning service for eligible open-source projects. The OSS Scanner is powered by their most capable models, including Claude Mythos. It scans codebases, identifies vulnerabilities, proposes patches, and sends reports directly to maintainers. As you read this, it has already identified real, high-severity issues in production software used by millions.